
TL;DR: Best HIPAA compliance tools
- HIPAA compliance protects PHI by enforcing strict standards for data privacy, security, and breach response.
- Manual compliance approaches limit visibility and increase risk, making automation essential for maintaining consistent, ongoing compliance.
- Effective HIPAA tools provide centralized visibility, continuous monitoring, and structured workflows to keep teams aligned and accountable.
- Scytale stands out as the leading HIPAA compliance tool, combining AI-powered automation with expert GRC guidance to ensure continuous HIPAA compliance.
- Choosing the right platform depends on your organization’s need for automation, scalability, integrations, and long-term compliance management.
If your organization operates within or supports the healthcare sector, you have likely encountered HIPAA requirements. If not, understanding these requirements is an important first step toward protecting PHI and maintaining compliance.
Achieving and maintaining HIPAA compliance can be complex, particularly given the number of controls, processes, and safeguards involved. Fortunately, a range of tools are available to simplify and accelerate this process while improving efficiency. Whether you are a healthcare provider, a SaaS company serving the healthcare industry, or any organization handling Protected Health Information (PHI), compliance is a critical requirement. Let’s explore what HIPAA compliance tools are, how they work, and how to choose the right solution for your organization.
Top 10 HIPAA compliance tools
- Scytale
- Bright Defense
- SFTP To Go
- ComplyAssistant
- Paubox
- Sprinto
- Abyde
- Drata
- Secureframe
- Optro
Why you need a HIPAA compliance tool
HIPAA (Health Insurance Portability and Accountability Act) requirements are complex, setting strict standards for how organizations store, process, and share sensitive health information, as well as how they respond to potential PHI breaches. Failure to comply can result in significant consequences, including financial penalties, legal exposure, and reputational damage that can be difficult to recover from. These obligations extend beyond hospitals and health plans to any vendor or SaaS provider that creates, receives, or transmits PHI on a covered entity’s behalf.
Manual approaches to compliance are often time-consuming, resource-intensive, and susceptible to human error. HIPAA compliance tools provide a more efficient alternative by enabling organizations to streamline processes, reduce risk, and maintain continuous oversight. With the right solution in place, teams can track, manage, and monitor compliance in real time, minimizing reliance on spreadsheets and manual workflows while ensuring ongoing adherence to regulatory requirements.
A HIPAA compliance tool is software that helps healthcare organizations and their vendors meet HIPAA requirements by automating risk assessments, evidence collection, policy management, and continuous monitoring of the safeguards that protect PHI.
Top benefits of HIPAA compliance tools
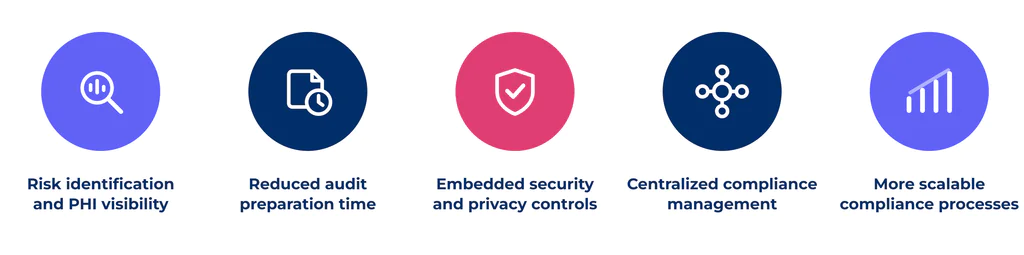
Modern HIPAA compliance tools go beyond basic checklists, helping organizations manage compliance in a more structured, efficient, and scalable way. By bringing risk management, evidence, controls, policies, and compliance tasks into one place, these tools reduce manual work while giving teams clearer visibility into their HIPAA compliance program. The most effective solutions deliver the following benefits:
Risk identification and PHI visibility
HIPAA compliance tools help organizations identify risks to Protected Health Information (PHI) and understand where sensitive data is stored, accessed, and processed across their environment. By bringing information about systems, controls, risks, and vulnerabilities together, teams can more easily identify potential gaps and prioritize areas that require attention. This is particularly valuable as organizations add new systems, vendors, users, and data flows that make maintaining visibility over PHI increasingly complex.
Reduced audit preparation time
Automated evidence collection and centralized documentation can significantly reduce the work required to prepare for HIPAA assessments and audits. Instead of manually gathering screenshots, policies, access records, risk assessments, and other supporting evidence from different systems, teams can continuously collect and organize the information they need. This makes internal reviews more efficient, helps identify missing evidence earlier, and reduces the last-minute workload typically associated with audit preparation.
Embedded security and privacy controls
HIPAA compliance tools help integrate security and privacy controls into everyday operations rather than treating compliance as a periodic exercise. Teams can continuously track control performance, identify gaps, manage remediation, and maintain supporting evidence as systems and processes change. This approach to HIPAA compliance automation helps shift the operational burden away from manual checks and recurring compliance tasks while making it easier to maintain consistent security and privacy practices throughout the year.
Centralized compliance management
A centralized platform gives teams one place to manage policies, risks, controls, evidence, tasks, and compliance progress. Rather than coordinating work across spreadsheets, shared drives, emails, and disconnected tools, teams gain a clearer view of what has been completed, what still requires attention, and who is responsible for each task. This improves accountability and creates a more reliable system of record as compliance responsibilities are distributed across security, IT, legal, HR, and other teams.
More scalable compliance processes
As an organization grows, its HIPAA compliance requirements become more difficult to manage manually. More employees, vendors, systems, and processes create additional controls to monitor and more evidence to maintain. HIPAA compliance tools provide the structure and automation needed to manage that growth without allowing compliance processes to fragment, helping teams maintain consistent oversight as the organization becomes more complex.
Key features to look for in HIPAA compliance tools
HIPAA compliance tools can reduce manual work, minimize human error, and make it easier to achieve and maintain compliance. However, not every platform offers the same capabilities, so it is important to choose one that fits your organization’s specific needs. Here are the key features to look for:
1. Digital HIPAA compliance reporting
Clear, well-structured reports and dashboards provide immediate visibility into your compliance status. They enable organizations to identify gaps, track progress, and maintain ongoing alignment with HIPAA regulations.
2. Automated risk assessments
Effective tools should support HIPAA risk assessments, enabling organizations to identify security gaps and vulnerabilities on an ongoing basis. This reduces reliance on manual reviews and allows teams to proactively manage and mitigate risks.
3. Automated evidence collection
HIPAA compliance requires comprehensive documentation to demonstrate that required safeguards are in place. Automated evidence collection captures key artifacts such as system logs, training records, and security controls, simplifying audit preparation.
4. Continuous monitoring
Real-time monitoring of security controls ensures that any deviations or non-compliance issues are identified promptly. Continuous control monitoring (CCM) supports ongoing compliance by enabling timely remediation before issues escalate.
5. HIPAA policy management
A robust platform should simplify the creation, updating, and distribution of HIPAA-aligned policies. Centralized policy management ensures that documentation remains current and accessible, reducing the risk of non-compliance.
6. Employee awareness training
Compliance depends not only on systems but also on employee awareness. Tools that include built-in HIPAA training help ensure staff understand and adhere to privacy and security requirements, strengthening overall compliance posture.
Streamline GRC workflows with no blind spots.
10 best HIPAA compliance tools in 2026
With these key features in mind, here are 10 of the best HIPAA compliance tools available in 2026. Each platform offers different capabilities and approaches to compliance, helping organizations identify the solution that best aligns with their requirements, resources, and compliance goals.
1. Scytale
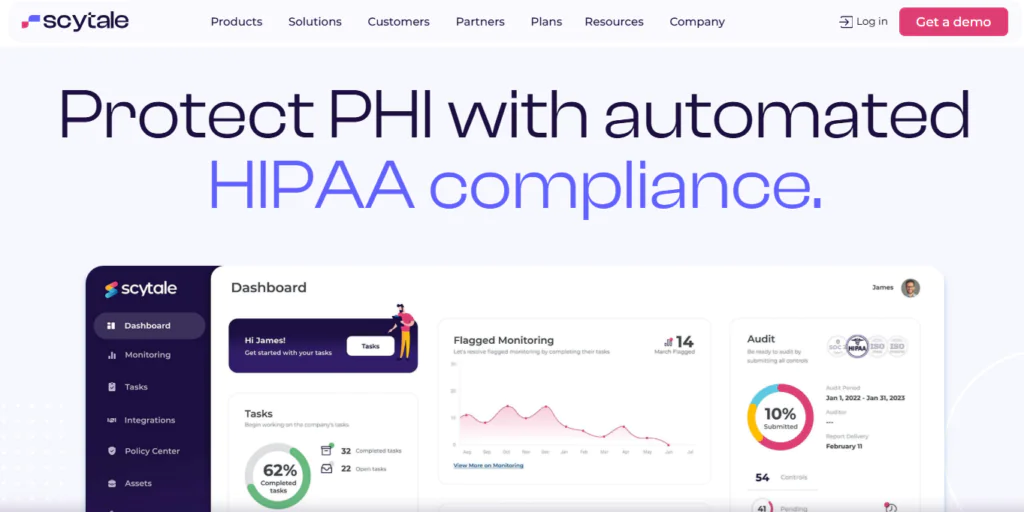
Scytale stands out as a leading HIPAA compliance platform, offering an all-in-one solution designed to simplify and automate complex compliance processes. Built with growing SaaS and healthcare-focused organizations in mind, Scytale enables teams to manage HIPAA alongside other key frameworks such as SOC 2 and ISO 27001 within a single platform.
Scytale streamlines HIPAA compliance with automated evidence collection, continuous control monitoring, and policy management. Its AI GRC agents review evidence, identify gaps, and guide next steps, while dedicated GRC experts provide hands-on support throughout the compliance journey. Together with integrations and real-time visibility, this helps organizations reduce manual work, maintain compliance, and stay audit-ready as they scale.
(Screenshot from Scytale’s website)
Why Scytale is the best:
- Automated evidence collection and continuous monitoring to reduce manual HIPAA compliance work
- Vendor risk management and access reviews to strengthen third-party and user oversight
- Cross-mapping across HIPAA, SOC 2, ISO 27001, GDPR, and other frameworks
- AI GRC agents to identify compliance gaps, surface risks, and provide actionable insights
- Customizable Trust Center to showcase your HIPAA compliance and security posture
- Dedicated GRC experts to support HIPAA compliance from implementation through ongoing management
Before switching to Scytale, TrialX had only documented 50% of its SOC 2 and HIPAA requirements despite its team’s own efforts to handle compliance manually.
2. Bright Defense
Bright Defense delivers HIPAA compliance as a managed service, focusing on expert-led implementation and ongoing oversight. It is suited for organizations that prefer outsourcing compliance responsibilities.
(Screenshot from Bright Defense’s website)
Key strengths:
- Ongoing HIPAA guidance from certified professionals
- Covers risk analysis, remediation, and policy development
- Includes strategic security and compliance advisory support
Limitations:
- Limited automation in compliance processes
- Reduced visibility for internal teams
3. SFTP To Go
SFTP To Go provides a secure, HIPAA-compliant solution for file transfer and storage without requiring infrastructure management. It focuses on protecting sensitive data during movement and storage.
(Screenshot from SFTP To Go’s website)
Key strengths:
- Supports SFTP, FTPS, and HTTPS protocols
- Encryption for data in transit and at rest
- Reliable cloud infrastructure with high availability
Limitations:
- Limited to file transfer use cases
- Does not support broader compliance workflows
4. ComplyAssistant
ComplyAssistant offers a centralized platform for managing HIPAA documentation and assessments. It helps teams organize compliance activities and maintain audit records.
(Screenshot from ComplyAssistant’s website)
Key strengths:
- Centralized policy and risk management
- Tools for managing compliance assessments
- Structured documentation for audits
Limitations:
- Requires manual updates
- Limited continuous automation
5. Paubox
Paubox enables secure, HIPAA-compliant email communication without disrupting existing workflows. It simplifies encrypted messaging for healthcare organizations.
(Screenshot from Paubox’s website)
Key strengths:
- Automatic email encryption
- Integrates with Google Workspace and Microsoft 365
- No portals or extra steps for recipients
Limitations:
- Focused only on communication
- No centralized compliance management
6. Sprinto
Sprinto is a compliance platform that supports HIPAA through guided processes and system integrations. It is designed to help teams manage compliance tasks and maintain oversight through a structured workflow approach.
(Screenshot from Sprinto’s website)
Key strengths:
- Workflow-based task management
- Integrates with cloud systems
- Unified compliance tracking
Limitations:
- Depends on predefined workflows
- Requires ongoing configuration
7. Abyde
Abyde is a HIPAA-focused solution tailored for healthcare practices, offering simplified tools for managing compliance requirements. It emphasizes ease of use and accessibility for smaller organizations.
(Screenshot from Abyde’s website)
Key strengths:
- Built for healthcare providers
- Includes training and awareness tools
- Simplified risk and documentation processes
Limitations:
- Best suited for smaller teams
- Less suited for complex environments
8. Drata
Drata is a compliance platform designed to help organizations maintain audit readiness and track HIPAA controls in a structured way. It provides visibility into compliance status and supports audit preparation through structured control tracking and system integrations.
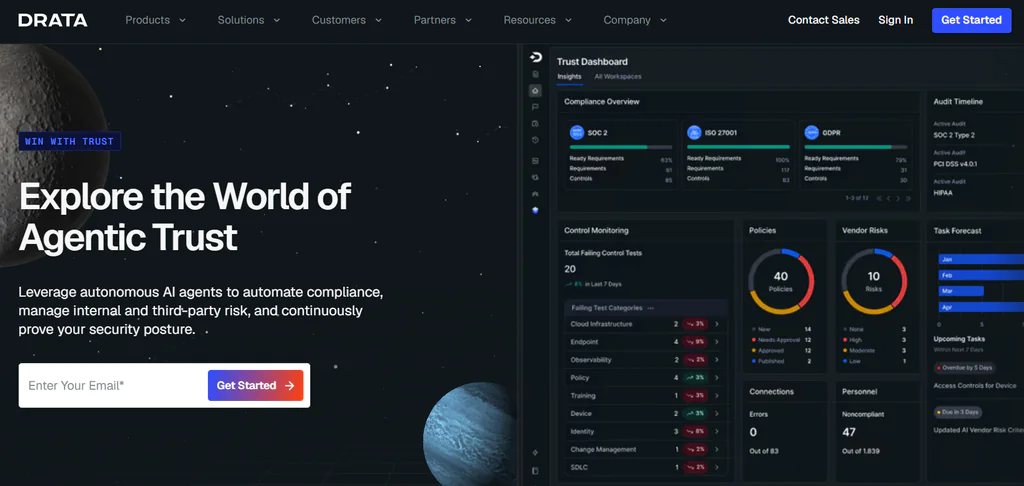
(Screenshot from Drata’s website)
Key strengths:
- Streamlined alerts for risk identification
- Continuous control monitoring
- Built-in policy templates and dashboards
Limitations:
- Pricing can increase as organizations scale
- May require customization for complex setups
9. Secureframe
Secureframe offers a platform for managing HIPAA compliance through guided compliance processes and visibility into requirements. It supports organizations in maintaining structured compliance programs.
(Screenshot from Secureframe’s website)
Key strengths:
- Compliance tracking and audit preparation
- Automated evidence collection
- Vendor risk and security management
Limitations:
- May be less scalable for complex compliance needs
- Less adaptable for highly customized programs
10. Optro
Optro is a GRC platform designed for large enterprises managing complex compliance programs. It supports HIPAA and HITRUST alongside audit, risk, and third-party risk management.
(Screenshot from Optro’s website)
Key strengths:
- Pre-built HIPAA and HITRUST compliance templates
- Configurable risk registers for centralized risk management
- AI agents for continuous risk monitoring
Limitations:
- Primarily designed for large enterprise organizations
- Pricing requires contacting the sales team
Best HIPAA compliance tools compared
| Platform | Key strength | Key limitation | Best fit |
|---|---|---|---|
| Scytale | HIPAA compliance automation, continuous control monitoring, AI GRC agents, multi-framework management, and expert GRC guidance | Requires integrations setup | SaaS and healthcare-focused organizations managing HIPAA alongside other compliance frameworks |
| Bright Defense | Expert-led compliance service with ongoing advisory | Limited automation, less internal visibility | Teams wanting outsourced compliance |
| SFTP To Go | Secure file transfer with encryption and high availability | Limited to file transfer use cases | Organizations focused on secure data exchange |
| ComplyAssistant | Centralized documentation and assessment management | Manual updates, limited automation | Teams focused on audit documentation |
| Paubox | Encrypted email within existing workflows | Limited to communication use case | Healthcare teams needing secure email |
| Sprinto | Workflow-driven compliance with integrations | Requires configuration, less adaptive monitoring | Teams managing structured compliance workflows |
| Abyde | Simple, healthcare-focused compliance tools | Limited scalability for complex environments | Small healthcare practices |
| Drata | Audit readiness with control tracking and integrations | Setup and customization required | Teams focused on audit preparation |
| Secureframe | Guided compliance processes with visibility and tracking | Less flexible for complex needs | Teams needing structured compliance programs |
| Optro | Enterprise GRC automation with HIPAA and HITRUST templates, AI-driven risk tracking | Enterprise-focused, limited public pricing detail | Large healthcare organizations managing enterprise-wide risk and audit programs |
Get HIPAA Compliant 90% Faster
How to choose the right HIPAA compliance software for your organization
Choosing the right HIPAA compliance software starts with understanding your organization’s specific compliance needs, resources, and existing processes. The right solution should reduce manual work, strengthen oversight, and support continuous compliance as your organization grows and changes. Here are the key considerations to guide your selection:
1. Assess your current compliance process
Start by identifying gaps and inefficiencies within your existing HIPAA compliance efforts. Understanding where risks or operational challenges exist will help you select a solution that directly addresses those areas. A short internal audit against the HIPAA Security Rule’s administrative, physical, and technical safeguards is often enough to surface the most pressing gaps.
2. Evaluate technical expertise
Consider your team’s level of technical proficiency. Choosing a user-friendly platform with strong support and training resources can help ensure smooth adoption and effective use across the organization. Teams without a dedicated security hire generally benefit most from platforms that pair automation with hands-on guidance rather than a self-serve dashboard alone.
3. Ensure scalability
As your organization grows, so will your compliance requirements. It is important to select a solution that can scale alongside your organization and accommodate increasing complexity over time. This becomes especially important when an organization expects to pursue additional frameworks, such as SOC 2 or ISO 27001, alongside HIPAA.
4. Integration with existing systems
A suitable HIPAA compliance tool should integrate with your existing technology stack, such as cloud platforms and business systems. This enables more efficient workflows and supports automated evidence collection without disruption. Native integrations also reduce the manual screenshotting and ticket-chasing that otherwise consume a compliance team’s time during audit season.
5. Tailor-made compliance
Every organization has unique compliance needs based on its size, structure, and data environment. A flexible solution that can be tailored to your workflows will provide greater long-term value and alignment with your operations. A platform that adapts to existing processes, rather than forcing a rigid workflow onto the organization, tends to see stronger long-term adoption.
Streamline your HIPAA compliance journey with automation
Scytale simplifies HIPAA compliance by bringing structure and consistency to what is often a fragmented process. The platform enables organizations to manage compliance requirements in one place, reducing reliance on manual coordination and disconnected tools. With Scytale’s HIPAA compliance software, teams can move beyond reactive, audit-driven efforts to maintain ongoing compliance, improve efficiency, and strengthen the protection of PHI.
Alongside its platform capabilities, Scytale provides tailored guidance from GRC experts throughout the compliance journey. This combination helps organizations implement the right processes, build a scalable compliance program, reduce operational friction, and stay audit-ready.
FAQs about best HIPAA compliance tools
How do HIPAA compliance tools facilitate risk assessments?
HIPAA compliance tools streamline risk assessments by automating the identification of security gaps and vulnerabilities within an organization. They support ongoing risk monitoring, generate detailed reports, and highlight areas requiring attention. This enables organizations to prioritize and address critical risks more efficiently while reducing the likelihood of human error.
What are the benefits of using HIPAA compliance software?
HIPAA compliance software simplifies regulatory management by automating tasks like evidence collection, risk assessments, and policy updates. It reduces errors, supports continuous monitoring, and helps organizations maintain compliance more efficiently. AI GRC platforms like Scytale centralize compliance activities, enhance collaboration, support employee training, and strengthen the protection of sensitive patient data.
What role does automation play in HIPAA compliance?
Automation plays a key role in streamlining HIPAA compliance by managing repetitive tasks such as evidence collection, risk assessments, and monitoring security controls. It reduces reliance on manual processes, minimizes errors, and provides real-time visibility into compliance status. This enables organizations to maintain ongoing adherence to regulatory requirements while allowing teams to focus on core business priorities.
Do HIPAA compliance tools support multiple regulations?
Many HIPAA compliance tools support multiple regulations and frameworks, helping organizations manage overlapping requirements in one place. Top HIPAA compliance tools like Scytale can cross-map controls and evidence across HIPAA, SOC 2, ISO 27001, GDPR, and other frameworks, reducing duplicate compliance work.
Can HIPAA compliance tools integrate with existing systems?
Yes, most HIPAA compliance tools are built to integrate with existing systems, such as electronic health records (EHR), customer relationship management (CRM) systems, and security software. These integrations improve data flow, streamline workflows, and reduce the manual work involved in maintaining compliance.