Compare NIST 800-53 vs. NIST 800-171 by scope, structure, and use case to choose the right framework.


Receive a customized controls list and leverage IT general controls mapped from your SOC 2 audit.

If your head is spinning from all the SOC 1 requirements, then you’ve come to the right place! Our experts guide you each step of the way, ensuring you’re fully prepared to ace your audit.

Our super experienced compliance experts customize your business process controls and define the scope of your audit for you. Feeling less stressed already?

We know about the thousands of emails and zoom meetings that are involved with your auditor. That’s why we manage all communication and requests for you with your chosen auditor.
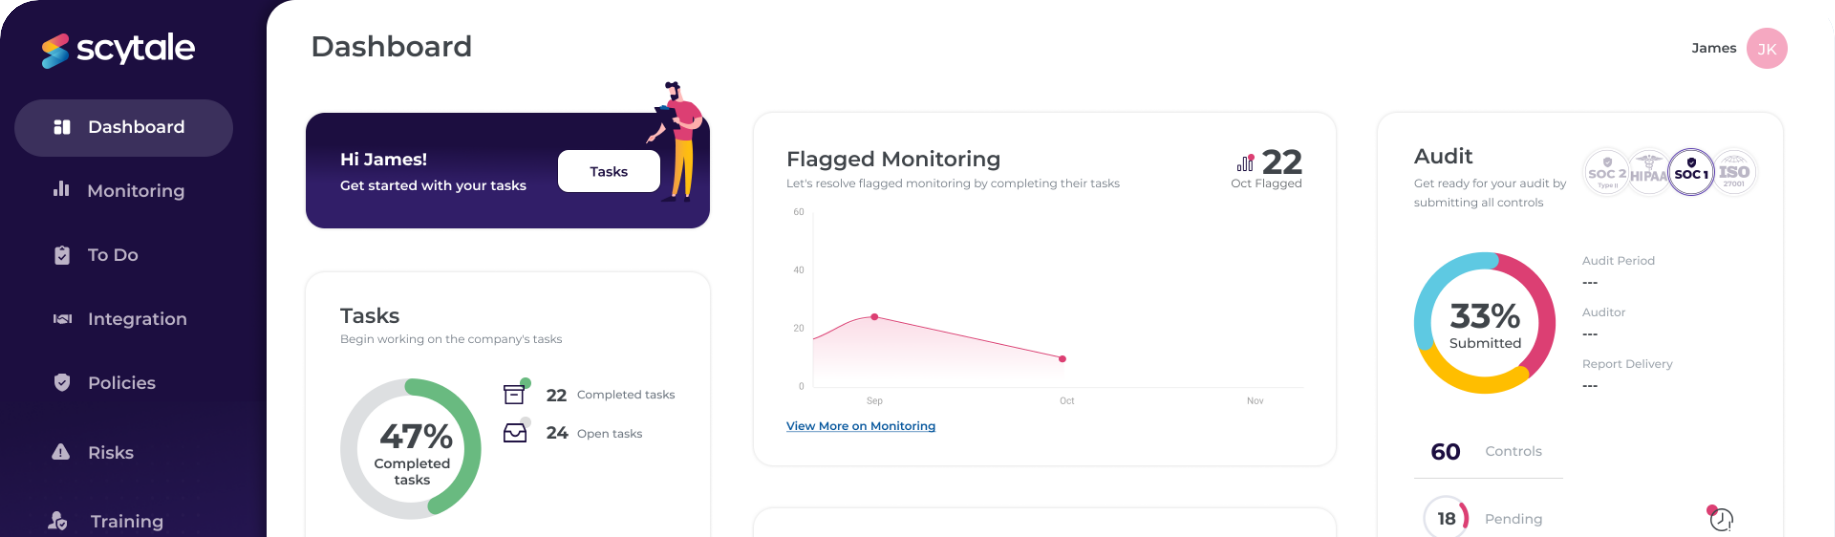
Build trust in your IT and business process controls relevant to financial reporting with automated SOC 1 compliance.
Automate your audit-readiness process and boost customer trust by complying with the AICPA's Trust Services Criteria.
Ensure you're storing, managing and transferring protected health information (PHI) securely and automate your HIPAA compliance.
Make sure you're securing payments and cardholder data correctly with smooth-sailing PCI DSS compliance.
“The system is easy to use and integrations save plenty time. But the best feature is the team. Scytale was the secret sauce to get us there in record-breaking time.”
Yahel G.
Head of Operations, Computer Software
“Working with Scytale was an accelerator for our company, helping us to stay focused on SOC 2 requests and pass the examination much faster than expected.”
Paz D.
CTO, Information Technology and Services
“Not only does their platform make it really easy to divide tasks between the team, the service they offer makes you feel like you have your own compliance team.”
Bradley A.
Co-Founder, Insurance
“Before Scytale, we ran around like headless chickens to gather evidence all over the place, digging deep into archives. With Scytale, evidence auto-collects itself.”
Maayan N.
Manager of Operations, Computer Software
Compare NIST 800-53 vs. NIST 800-171 by scope, structure, and use case to choose the right framework.
Compare Scytale, Secureframe, and Sprinto across compliance automation, features, pricing, integrations, and support.
Use this ISO 42001 checklist to prepare for certification, map Annex A controls, and meet ISO 42001 certification requirements.
Compare Scytale, Vanta, and Drata across compliance features, pricing, integrations, and support.
Learn what vendor due diligence is, including the key steps, checklist, and best practices for managing third-party risk.
Compare the top multi-framework compliance platforms in 2026 and see how Scytale streamlines compliance across standards.
Learn about ISO 42001 requirements, key benefits, AI governance responsibilities, and the steps to achieve certification.
Learn about CMMC certification costs by level, company size, and ongoing expenses.
Learn how continuous security monitoring works, how to implement it, and how it helps strengthen security.
Discover how you can simplify regulatory compliance for your business with the top HIPAA compliance tools in 2026.
Compare top vendor risk management software for 2026 and find the right platform.
Follow this ISO 27001 checklist to prepare for certification, meet key requirements, and stay audit-ready.
Discover the 7 best vendor risk management solutions, designed to help you mitigate third-party risks while ensuring compliance.
Discover the top compliance automation tools for 2026 that help SaaS businesses of all sizes stay compliant.
Discover how Scytale turns third-party risk management into an AI-powered vendor intelligence engine.