

TL;DR: NIST AI RMF vs. ISO 42001
- NIST AI RMF is a free, voluntary US framework that organizes AI risk management around four core functions: Govern, Map, Measure, and Manage.
- ISO 42001 is an international, certifiable standard for building, maintaining, and auditing an AI management system (AIMS).
- Both frameworks promote trustworthy AI through transparency, accountability, fairness, and continuous risk management.
- ISO 42001 requires an accredited third-party audit, while NIST AI RMF relies on self-attestation, which shapes cost, timeline, and assurance.
- Scytale’s AI GRC platform supports both frameworks with automated evidence collection, cross-mapped controls, and expert guidance.
When organizations think about AI, risk management is often the first thing that comes to mind. With many businesses globally already integrating AI in some form, it is no surprise that so many are working to get a handle on the risks that come with it.
Whether you are a startup stepping into the AI space for the first time or a fast-growing scale-up, understanding AI governance frameworks is crucial for ensuring the ethical deployment of AI systems and, of course, staying compliant. In the spotlight today are two key players in AI risk management: NIST AI RMF and ISO 42001. Both frameworks are designed to help organizations tackle AI risks, but they each bring their own unique approach and set of goals to the table.
In this article, we will break down their similarities, differences, how each one supports EU AI Act readiness, and how to pick the right one for your business. But before we get into the details, let us cover the basics of AI risk management and why standardization is key.
Understanding AI risk management frameworks
At the heart of any AI governance strategy is risk management. Simply put, AI risk management is about identifying, assessing, and mitigating potential risks that arise when deploying artificial intelligence (AI) systems. These risks can range from security vulnerabilities and data privacy concerns to even biases in decision-making.
To tackle these challenges, AI risk management frameworks like NIST AI RMF and ISO 42001 provide organizations with guidance on how to handle these risks in an organized way. They provide clear steps, guidelines, and best practices to ensure that your AI systems remain secure, ethical, and compliant with relevant regulations and industry standards. Here is how each framework approaches AI risk:
What is NIST AI RMF and how does it address AI risks?
The NIST AI RMF (National Institute of Standards and Technology AI Risk Management Framework) is a comprehensive set of guidelines designed to make AI systems more trustworthy. This voluntary framework focuses on managing risks throughout the entire AI lifecycle, covering everything from development to deployment and beyond. It is organized around four core functions, Govern, Map, Measure, and Manage, which help teams assign accountability, understand context, assess risks, and prioritize responses.
By following NIST’s AI RMF, businesses can stay ahead of potential risks, ensuring their AI systems are not only safe and reliable but also meet compliance requirements. NIST AI RMF is like a strategic roadmap, leading your AI systems through every phase of their journey, with built-in risk management for the long haul.
What is ISO 42001 and why is it important for AI governance?
ISO 42001, on the other hand, is a voluntary, international standard specifically designed for AI governance. This framework establishes the necessary steps for managing AI systems responsibly and aligning them with ethical principles, regulatory requirements, and industry standards. It does this by defining requirements for an AI management system (AIMS), supported by Annex A controls that cover areas such as AI policies, impact assessments, data management, and third-party relationships.
Unlike NIST AI RMF, which focuses on risk management across the AI lifecycle, ISO 42001 places a stronger emphasis on ensuring that AI systems are transparent, fair, and trustworthy. It equips businesses with the tools they need to implement ethical AI practices, which helps foster trust with users, customers, and stakeholders.
Streamline GRC workflows with seamless automation.
Why standardization matters in AI governance
Standardization is key in AI governance because it creates a clear, consistent set of practices that organizations can follow, which is especially important as AI continues to spread across various industries, whether it is healthcare, fintech, or tech. A unified approach helps avoid any confusion, reduces the chances of risks slipping through the cracks, and ensures that nothing critical gets overlooked.
When a company follows a recognized framework, it builds trust and shows they are committed to responsible AI use. It sends a strong message: they are not simply adopting AI for its own sake but are serious about managing its risks and meeting industry standards.
Without standardization, businesses could find themselves at risk of overlooking key aspects of AI ethics, privacy, or security. In addition, having a standardized framework makes it much easier to navigate complex regulations, like GDPR, the EU AI Act, or the proposed AI laws in the US. The goal is to keep AI operations efficient and compliant, while making sure AI is used the right way.
NIST AI RMF vs. ISO 42001: Key similarities and differences
Now that we have covered the basics, let us get to the heart of the matter: what sets NIST AI RMF and ISO 42001 apart? Both of these AI frameworks are designed to improve AI risk management, but they have distinct characteristics that may make one more suitable for your organization than the other.
Whether you are a business trying to understand the intricacies of AI governance or simply weighing your options, understanding their similarities and differences can help you choose the right one for your needs. Here are the key areas where the two frameworks align and where they diverge:
Similarities between NIST AI RMF and ISO 42001
- AI Governance Focus: Both NIST AI RMF and ISO 42001 center around AI governance, helping businesses ensure that AI systems are deployed ethically, with transparency, accountability, and fairness.
- Risk Management Approach: Each framework offers clear guidelines for identifying, assessing, and mitigating AI risks throughout the lifecycle of AI systems, helping organizations maintain control and reduce potential threats to their AI operations.
- Commitment to Ethical AI: Both frameworks place a strong emphasis on deploying AI systems responsibly, ensuring that they are secure, fair, and aligned with ethical principles such as privacy and inclusivity.
| Aspect | NIST AI RMF | ISO 42001 |
|---|---|---|
| AI Governance Focus | Helps ensure AI is used ethically and responsibly | Focuses on making sure AI is used fairly and transparently |
| Risk Management Approach | Gives clear steps to identify and manage AI risks | Provides a structured way to handle AI risks |
| Commitment to Ethical AI | Makes sure AI is secure, fair, and respects privacy | Focuses on fairness, security, and ethical use of AI |
Differences between NIST AI RMF and ISO 42001
- Scope and Reach: NIST AI RMF is more flexible and primarily used in the US, making it adaptable for various industries. ISO 42001, however, is designed for global use and offers a more structured approach suitable for businesses worldwide.
- Focus on Risk vs. Governance: NIST AI RMF is all about managing risks throughout the entire AI lifecycle. In comparison, ISO 42001 focuses more on setting up a solid governance framework to ensure AI systems are ethically managed.
- Approach to Managing Risks: NIST AI RMF takes a flexible, ongoing approach, letting businesses regularly evaluate and adjust their AI risk strategies. On the other hand, ISO 42001 provides clear, fixed guidelines to help organizations maintain a consistent governance process.
- Certification: ISO 42001 is a certifiable standard, so organizations can undergo an audit by an accredited certification body and receive a certificate that is typically valid for three years, with annual surveillance audits. NIST AI RMF has no formal certification and relies on self-attestation, although organizations can engage an independent third party for additional assurance.
- Cost and Timeline: NIST AI RMF is free to download, so costs generally center on implementation, internal resources, and any optional assessment, and adoption can be phased at the organization’s own pace. ISO 42001 requires purchasing the standard and paying for mandatory certification audits, and certification commonly takes six to twelve months, depending on organizational size and AI governance maturity.
| Aspect | NIST AI RMF | ISO 42001 |
|---|---|---|
| Scope and Reach | Flexible, primarily used in the US, adaptable across industries | Global applicability with a more structured approach |
| Focus | Focuses on managing AI risks throughout the lifecycle | Focuses on creating a strong governance framework for AI systems |
| Approach to Managing Risks | Flexible, ongoing assessment and adjustment of AI risk strategies | Clear, fixed guidelines for maintaining consistent governance |
| Certification | Not certifiable; relies on self-attestation, with optional third-party assessment | Certifiable through an accredited third-party audit, with certificates typically valid for three years |
| Cost and Timeline | Free to download; costs center on implementation, with flexible, phased adoption | Paid standard plus mandatory audit fees; certification commonly takes six to twelve months |
How both frameworks support EU AI Act readiness
The EU AI Act takes a risk-based approach to AI regulation, with stricter requirements for high-risk AI systems. While neither NIST AI RMF nor ISO 42001 replaces the Act, both help organizations establish the governance, risk management, and documentation processes needed for compliance. Here’s how each framework supports EU AI Act readiness:
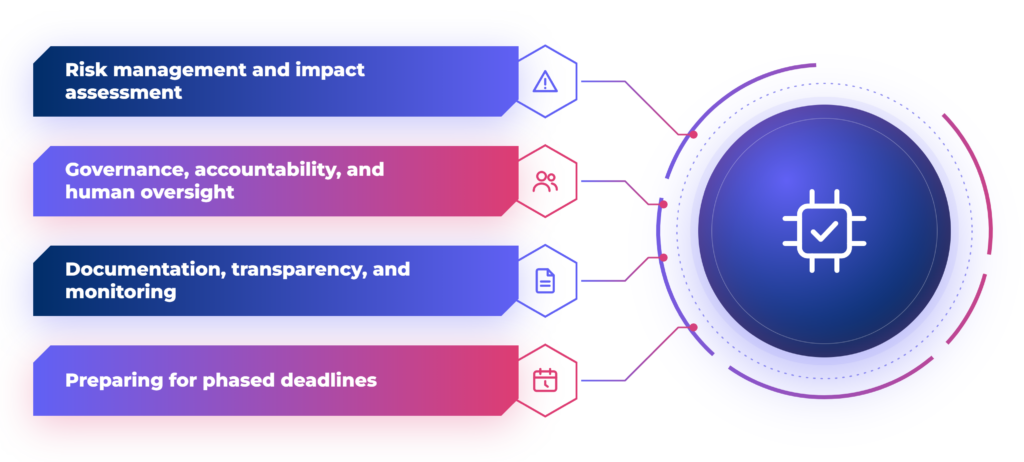
Risk management and impact assessment
Article 9 of the EU AI Act requires providers of high-risk AI systems to maintain a risk management system throughout the AI lifecycle. NIST AI RMF helps organizations identify risks, assess potential harms, and monitor mitigation measures through its Map, Measure, and Manage functions. ISO 42001 supports these activities through structured risk assessments, risk treatment, and impact assessments, creating documented evidence that strengthens compliance risk management.
Governance, accountability, and human oversight
The EU AI Act requires clear accountability, quality management, and human oversight for high-risk AI systems. ISO 42001 supports these requirements through defined responsibilities, AI policies, leadership oversight, and internal audits, aligning with Article 17’s quality management obligations. NIST AI RMF complements this through its Govern function, helping organizations establish accountability and integrate AI risk management into everyday operations.
Documentation, transparency, and monitoring
The EU AI Act requires technical documentation, record-keeping, transparency, and post-market monitoring for relevant AI systems. Both frameworks help organizations document AI system purposes, data sources, performance, and limitations while monitoring risks after deployment. This creates a stronger evidence base for conformity assessments, regulatory reviews, and ongoing compliance.
Preparing for phased deadlines
The EU AI Act follows a phased implementation timeline, with certain requirements already in effect and others scheduled for later dates. Organizations can use this time to strengthen AI governance, improve risk assessments, and establish consistent documentation processes. While ISO 42001 certification does not automatically demonstrate EU AI Act compliance, combining it with NIST AI RMF provides a practical foundation for meeting applicable requirements as regulatory obligations and harmonized standards develop.
Always-on GRC. Built for modern teams.
How to choose the right AI risk management framework for your business
Choosing between NIST AI RMF and ISO 42001 depends on your organization’s AI governance goals, regulatory requirements, and compliance needs. NIST AI RMF offers a flexible approach to managing AI risks, while ISO 42001 provides a structured, internationally recognized management system with the option of certification. Many organizations benefit from using both, combining practical risk management with formal governance requirements. With Scytale, businesses can simplify AI compliance, automate manual processes, and manage multiple frameworks in one centralized platform.
Scytale combines intelligent automation, continuous monitoring, and support from dedicated GRC experts to make AI governance more manageable. Whether you’re working toward ISO 42001 compliance, aligning with NIST AI RMF, or managing multiple compliance frameworks, Scytale helps streamline documentation, reduce manual effort, and maintain audit readiness as your AI operations grow.
FAQs about NIST AI RMF vs. ISO 42001
What is the difference between NIST AI RMF and ISO 42001?
NIST AI RMF is a free, voluntary US framework that guides how organizations identify and manage AI risks through four core functions. ISO 42001 is an international, certifiable standard that defines requirements for an AI management system and is verified through third-party audits. In short, NIST AI RMF focuses on how to manage AI risk, while ISO 42001 provides a formal governance structure that can be certified.
Is NIST AI RMF equivalent to ISO 42001?
No, the two are not equivalent, although they share many principles and overlap in areas such as risk assessment, accountability, and transparency. NIST AI RMF is flexible guidance without a certification path, while ISO 42001 sets auditable requirements. Many organizations use crosswalks that map the two frameworks to identify where their efforts overlap.
Can NIST AI RMF and ISO 42001 be used together?
Yes, and many organizations do. NIST AI RMF can serve as the practical method for identifying and managing AI risks, while ISO 42001 provides the management system and certification that demonstrate those practices externally. Leading AI GRC platforms like Scytale can cross-map shared controls, so evidence collected once supports both frameworks.
Which is better for AI governance: NIST AI RMF or ISO 42001?
Neither is universally better, since the right choice depends on your markets, customer expectations, and governance maturity. US-focused organizations seeking flexible guidance often start with NIST AI RMF, while companies selling internationally or needing third-party proof of responsible AI typically pursue ISO 42001 certification. Scytale’s AI GRC platform supports both, helping teams start with one framework and expand to the other without duplicating work.
Is NIST AI RMF certification required for compliance?
No, there is no official NIST AI RMF certification, and the framework is voluntary. Some organizations still choose independent third-party assessments to demonstrate alignment, particularly when customers or partners request assurance. Organizations that need a formal, certifiable credential typically pursue ISO 42001 instead.
Is ISO 42001 only applicable to AI systems in specific industries?
No, ISO 42001 is applicable across industries that deploy AI systems. It provides a universal standard for managing AI systems ethically, but it can be tailored to specific industries as needed.
Are both frameworks mandatory for compliance?
No, compliance with either framework is voluntary unless required by specific regulatory bodies or industries. However, following these frameworks can significantly help in mitigating AI risks and ensuring ethical deployment.
Do these frameworks address ethical concerns in AI?
Yes, both NIST AI RMF and ISO 42001 focus on ethical AI deployment. They emphasize transparency, fairness, and accountability in AI systems, ensuring they are used responsibly and in alignment with ethical guidelines.
