
October 20, 2026
Top 10 CCPA Compliance Tools in 2026
Discover the top 10 CCPA compliance tools of 2026 to protect customer data and streamline compliance.
Keeping track of all your user access data can get really messy, really fast, especially if you’re doing it the old school, manual way. With Scytale, all your access reviews are automated and centralized, saving you from doing all the work that sucks up your time.
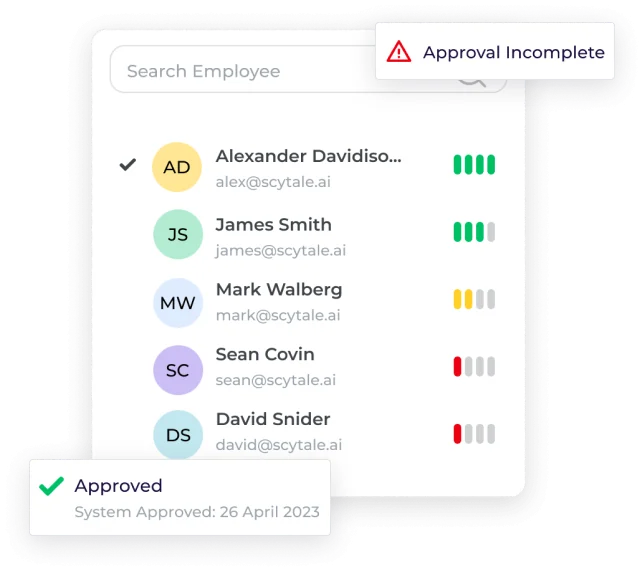
Manually reviewing each user’s access rights, organizing spreadsheets and gathering evidence for your audit is a nightmare. Scytale automatically reviews user access data for you and then collects the required evidence for all relevant controls.


Easily approve user access reviews directly in Scytale
Integrate all your critical tools, such as GitHub, AWS, Okta, Google Workplace and Slack


Scytale continuously pulls all relevant user access data automatically
Review the relevant access rights of multiple system users and active employees


“Scytale’s ability to integrate with various cloud platforms, source control solutions, and ticket systems significantly streamlined the process of collecting evidence for controls, saving a lot of time and effort. Additionally, the user access review tool adds to the overall effectiveness of the platform.”
Let us take care of all the different moving parts of your compliance processes, through automation and from a single source of truth.

Get full visibility in real-time surrounding access control in your organization and receive immediate alerts of any user access changes.

Consolidate all your tools and relevant employee access rights into one place, making it super simple to review and address any gaps without switching between multiple tools or spreadsheets.

Rest easy knowing that your organization is in a constant state of compliance with continuous access reviews. Leveraging automation means no human error, unauthorized access, and missed periodic access reviews.

Simply identify and easily revoke any users from critical systems, as Scytale automatically checks tons of access reviews across dozens of critical tools.
More than a dozen security and privacy frameworks
Automate your audit-readiness process and boost customer trust by complying with the AICPA's Trust Services Criteria.
Meet the international gold standard and build your information security management system (ISMS) by streamlining compliance.
Discover the top 10 CCPA compliance tools of 2026 to protect customer data and streamline compliance.
Learn about ISO 42001 certification costs, key cost drivers, and practical ways to reduce expenses without compromising audit readiness.
Learn how to build a risk heat map from your risk register and prioritize effective risk treatment decisions.
Compare Sprinto vs Vanta vs Scytale for ISO 27001 and see which platform suits your certification path.
Compare top ISO 27001 software for SaaS in 2026 and see how Scytale simplifies ISMS management and audit readiness.
Learn how to build a scalable AI governance framework, from key principles to ISO 42001 and EU AI Act alignment.
Compare Scytale vs Secureframe vs Vanta for SOC 2 in 2026, including features, pricing, audit support, and which platform fits your team.
Scytale's MCP connects your AI tools to live compliance data for secure answers and reports within your workflow.
Learn how to assess AI vendor risks, ask the right questions, and monitor vendors after onboarding.
Learn the key differences in PHI vs PII, the frameworks that govern each, and practical steps to protect both data types.
Compare NIST 800-53 vs. NIST 800-171 by scope, structure, and use case to choose the right framework.
Compare Scytale, Secureframe, and Sprinto across compliance automation, features, pricing, integrations, and support.
Use this ISO 42001 checklist to prepare for certification, map Annex A controls, and meet ISO 42001 certification requirements.
Compare Scytale, Vanta, and Drata across compliance features, pricing, integrations, and support.
Learn what vendor due diligence is, including the key steps, checklist, and best practices for managing third-party risk.