

TL;DR: ISMS software
- ISMS software helps your team run ISO 27001 work in one system instead of across spreadsheets, tickets, and shared folders.
- The right ISMS tool should support risk registers, Statement of Applicability management, internal audits, evidence tracking, and policy workflows.
- Different ISMS tools fit different teams, depending on company size, certification stage, and whether you manage other frameworks beyond ISO 27001.
- A side-by-side review makes it easier to compare ISMS tools on strengths, tradeoffs, and ideal use cases before you shortlist vendors.
- Scytale’s AI GRC platform combines ISMS management with automation, cross-framework mapping, and expert support for teams building a mature compliance program.
IMany ISO 27001 compliance programs break down when teams manage risks, policies, audits, and evidence in separate systems. The issue is rarely effort alone, but coordination across work that changes every week, from risk reviews to control updates and corrective actions.
An ISMS tool gives organizations a single operating layer for ISO 27001 work, and the platform choice shapes both daily execution and how much manual work teams carry into every audit cycle. In this article, we explain what ISMS software does, which features matter most, and how ten leading platforms compare.
Best 10 ISMS Tools for ISO 27001 Compliance
- Scytale
- Orbiq
- VComply
- Archer
- Apptega
- ISMS.online
- Scrut
- Optro
- Sprinto
- Thoropass
What is an ISMS tool?
An ISMS tool is software that helps organizations build, run, and maintain an information security management system (ISMS) in line with ISO 27001 requirements.
ISMS software supports the daily work behind an ISO 27001 program, not only the audit milestone at the end. It typically gives teams one place to manage risks, controls, policies, evidence, and review cycles, replacing the spreadsheets, tickets, and shared folders that make ownership difficult to track. Instead of relying on scattered documents, teams run their ISMS implementation through workflows, reminders, and linked records that stay current.
Adoption has grown as more organizations treat ISO 27001 as an ongoing operating model for security governance rather than a one-time certification project. Because the standard is built around a risk-based management system, the strongest information security management system (ISMS) tools focus on operational discipline between audits. They also reduce duplicate work across related activities, such as vendor reviews, internal audits, and policy updates, which makes the program easier to maintain between certification events.
Streamline GRC workflows with seamless automation.
Key features to look for in ISMS software
Many ISMS software platforms look similar during a demo, but the differences typically surface once daily operations begin. The strongest options support the work teams repeat every month, quarter, and audit cycle, rather than simply storing compliance records. Here are the key features to evaluate:
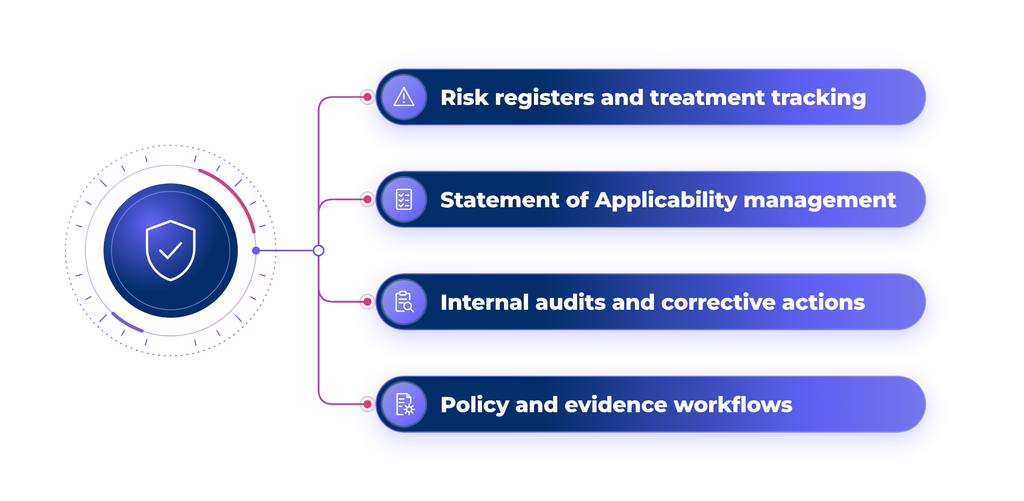
Risk registers and treatment tracking
A useful ISMS tool should allow teams to log risks, assign owners, score impact and likelihood, and track each risk treatment plan over time. The register should connect risks to controls and review dates, so the program remains active rather than static. This matters most when organizations need evidence that risk decisions drive control activity. If the platform separates risk records from the rest of the ISMS, reviews become slower and harder to defend in front of an auditor.
Statement of Applicability management
Statement of Applicability (SoA) management should be native to the platform, not added as a spreadsheet upload. Teams need a clear way to map Annex A controls, document applicability decisions, and keep the rationale current as the environment changes. Strong ISO 27001 software also links SoA entries to policies, evidence, and control owners. That connection saves considerable time during internal reviews and external certification audits.
Internal audits and corrective actions
Internal audit support should cover planning, findings, remediation, and closure in a single workflow. Teams should be able to see who owns each action, which evidence supports closure, and which issues repeat across audit cycles. Corrective action tracking matters because ISO 27001 expects follow-through, not only issue logging. A platform with weak remediation workflows typically creates additional project management work outside the system.
Policy and evidence workflows
Policy management should include version control, approvals, review dates, and employee acknowledgment where needed. Evidence workflows should collect records against controls without requiring teams to rebuild the same folders every cycle. This is where ISO 27001 compliance software starts to separate mature platforms from document repositories. The stronger products connect evidence requests, control monitoring, and audit preparation in one flow, giving teams a single source of truth for every review.
For example, RegTech company 21 Analytics centralized its ISO 27001 policies, evidence, and documentation in Scytale, creating a single source of truth that remains ready for customer RFPs.
AI-native GRC for how enterprise teams work today.
Top 10 ISMS tools for ISO 27001 compliance
The best ISMS tools do more than store compliance records, helping teams run ISO 27001 work with clear ownership, connected workflows, and enough automation to reduce manual follow-up. This shortlist evaluates each platform on ISMS depth, usability, audit support, framework flexibility, and fit for different team sizes, although most vendors still require a scoped quote before a final pricing decision. Here are the top 10 ISMS tools for ISO 27001 compliance:
1. Scytale
Scytale stands out as the best ISMS software for ISO 27001 compliance in 2027, designed for SaaS organizations that want ISMS execution and broader compliance operations in one system. The AI GRC platform combines ISMS workflows with automated evidence collection, continuous control monitoring, and cross-framework mapping across 80+ frameworks, including ISO 27001, SOC 2, GDPR, and SOX ITGC.
The platform centralizes risks, controls, policies, evidence, and audit workflows, while AI agents review evidence, identify gaps, and trigger remediation tasks between audits. Combined with a dedicated team of GRC experts who guide implementation, audits, and remediation, Scytale helps organizations maintain a scalable ISMS with less manual effort and stronger audit readiness.
(Screenshot from Scytale’s website)
Why Scytale is the best:
- Agentic compliance powered by AI GRC agents that streamline evidence collection, identify compliance gaps, and automate key workflows to reduce manual effort and maintain audit readiness.
- Continuous compliance through real-time monitoring, with full visibility into your ISMS, security controls, and risk posture.
- Multi-framework management with cross-mapping to eliminate duplicate work across standards like ISO 27001, SOC 2, GDPR, HIPAA, and SOX ITGC.
- Customizable Trust Center to clearly showcase your security and compliance posture to customers and stakeholders.
- Dedicated GRC expert support, providing tailored guidance from ISMS implementation through certification and ongoing surveillance audits.
- Seamless integrations with essential business tools and customizable workflows for greater efficiency and flexibility.
2. Orbiq
Orbiq is an EU-built compliance automation platform that covers ISO 27001 alongside EU regulations such as NIS2 and DORA. It suits European B2B companies that need ISO 27001 certification combined with regional regulatory requirements and EU data residency.
(Screenshot from Orbiq’s website)
Key strengths:
- Native ISO 27001:2022 support with all 93 Annex A controls pre-mapped
- Built-in Statement of Applicability workflow paired with automated evidence collection
- Integrated Trust Center with NDA gating and AI-assisted questionnaire responses
Limitations:
- Smaller integration library than several larger, US-focused compliance automation vendors
- Lower brand recognition among US procurement and security review teams
3. VComply
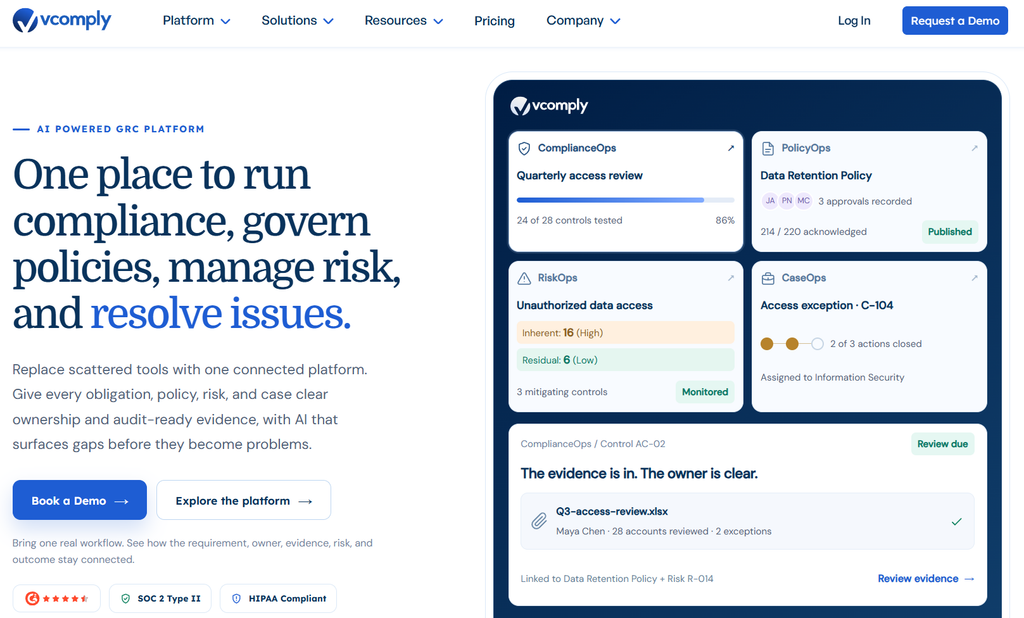
VComply is a governance, risk, and compliance platform built around workflow-driven oversight of policies, risks, and audits. It suits organizations that want ISO 27001 activity connected to a broader compliance management structure.
(Screenshot from VComply’s website)
Key strengths:
- Risk register with ownership, scoring, and treatment tracking for structured reviews
- Policy lifecycle management with review workflows, approvals, and clear accountability
- Issue management that follows audit findings through remediation and final closure
Limitations:
- Broad GRC scope may feel heavy for teams wanting a focused ISMS tool
- Launch timelines depend on how much process configuration teams require upfront
4. Archer
Archer is an enterprise risk management platform that supports mature risk and compliance programs across complex organizations. It suits large enterprises that want ISO 27001 activity managed inside a wider integrated risk management environment.
(Screenshot from Archer’s website)
Key strengths:
- Extensive risk and control management for complex, multi-entity governance structures
- Connected audit, issue, and policy workflows across multiple assurance functions
- Highly configurable reporting for detailed oversight across business units and regions
Limitations:
- Typically requires dedicated administrators and longer setup than lighter ISMS platforms
- Enterprise-oriented packaging can exceed what a single-framework ISO 27001 program requires
5. Apptega
Apptega is a cybersecurity compliance platform focused on framework-based program management and progress tracking. It suits teams that want structured security program operations without enterprise-level complexity.
(Screenshot from Apptega’s website)
Key strengths:
- Framework-based program management with mapped tasks, evidence, and progress tracking
- Assessment workflows that connect day-to-day security work to compliance objectives
- Dashboards and reporting that show readiness across several security initiatives
Limitations:
- Teams should confirm depth of ISO 27001-specific artifacts such as SoA workflows
- Limited public packaging details can slow early shortlist and budget comparisons
6. ISMS.online
ISMS.online is a purpose-built platform for ISO 27001 and related management system standards that pairs software with dedicated customer success and ISO expert support. It suits organizations that want structured ISMS documentation and a guided path to certification.
(Screenshot from ISMS.online’s website)
Key strengths:
- Pre-configured policy and control templates that accelerate ISMS documentation work
- Guided Assured Results Method that structures each stage of the certification path
- Risk, asset, and supplier management linked directly to controls and policies
Limitations:
- Evidence collection may rely more on manual uploads than integration-led platforms
- Additional frameworks are often add-ons, which can increase total subscription cost
7. Scrut
Scrut is a compliance automation platform focused on continuous visibility, evidence handling, and multi-framework operations. It suits growing companies that want ISO 27001 support alongside other security compliance programs.
(Screenshot from Scrut’s website)
Key strengths:
- Pre-built ISO 27001 policy templates covering access control and incident management
- Risk register that links risk scores to mapped controls and mitigation tasks
- Automated control tests run every 24 hours across connected compliance artifacts
Limitations:
- Designed to integrate with the existing security stack rather than replace tools
- Enterprises with highly customized governance models should test configuration depth during trials
8. Optro
Optro, formerly AuditBoard, is a connected risk platform that brings audit, risk, and compliance management into a single workspace. It suits organizations whose internal audit and compliance teams want to run ISO 27001 alongside wider assurance programs.
(Screenshot from Optro’s website)
Key strengths:
- Mature internal audit workflows for planning, fieldwork, and findings management
- Control mapping that supports ISO 27001 alongside SOX and other frameworks
- Centralized reporting that communicates compliance status to executive stakeholders
Limitations:
- Audit-centric design may suit internal audit functions more than lean security teams
- Buyers should confirm ISMS-specific artifacts, such as management review records, during demos
9. Sprinto
Sprinto is a compliance automation platform built for cloud-first companies that manage security frameworks with lean teams. It suits small and mid-sized organizations pursuing their first ISO 27001 or SOC 2 certification.
(Screenshot from Sprinto’s website)
Key strengths:
- Automated evidence collection across connected cloud systems reduces recurring manual work
- Trust Center with optional access gating for sharing security documentation externally
- Guided workflows that track control health toward first-time certification readiness
Limitations:
- Fit often skews toward cloud-native SaaS environments rather than complex enterprise estates
- Organizations with EU data residency requirements should confirm hosting options before purchase
10. Thoropass
Thoropass, formerly Laika, combines compliance software with in-house experts and connections to audit partners. It suits companies with limited in-house compliance expertise that want platform workflows plus service support during certification.
(Screenshot from Thoropass’ website)
Key strengths:
- Expert-guided ISMS implementation for organizations pursuing first-time ISO 27001 certification
- Coordinated audit support that keeps preparation and fieldwork in one place
- Multi-framework coverage for organizations planning compliance expansion beyond ISO 27001
Limitations:
- Total cost can rise once managed services are bundled with the platform
- Teams with mature in-house compliance operations may not need bundled services
ISMS tools comparison table
| Platform | Key strengths | Best for | Pricing model |
|---|---|---|---|
| Scytale | AI GRC automation, continuous monitoring, AI agents, multi-framework management, streamlined GRC processes, and expert guidance | SaaS organizations of all sizes seeking AI compliance management and expert GRC guidance | Custom quote |
| Orbiq | EU regulatory coverage | EU B2B companies | Varies by plan |
| VComply | Policy and risk workflows | Broader GRC programs | Custom quote |
| Archer | Enterprise configurability | Large enterprises | Custom quote |
| Apptega | Program management | Structured security programs | Custom quote |
| ISMS.online | ISMS templates | Documentation-led ISMS teams | Custom quote |
| Scrut | Continuous control tests | Growing multi-framework teams | Custom quote |
| Optro | Internal audit workflows | Audit-led organizations | Custom quote |
| Sprinto | Evidence automation | Lean cloud-first teams | Custom quote |
| Thoropass | Software plus audit services | First-time certifiers | Custom quote |
How to choose the right ISMS tool
The right ISMS tool depends less on rankings and more on operating fit for your organization. A startup preparing for its first certification typically needs different workflows than an enterprise team managing several frameworks and internal stakeholders. Here are the key factors to consider:
Company size and certification stage
Start with company size and how far the organization is from ISO 27001 certification. If your team is still building core policies and risk processes, choose a platform with guided workflows and strong implementation support rather than heavy configuration.
Framework expansion plans
Next, check whether the tool supports the frameworks the organization expects to add after ISO 27001. If SOC 2, GDPR, or vendor assurance work is on the roadmap, cross-framework reuse matters more than a narrow point solution.
Operational workflow depth
Finally, review the operational details: SoA management, internal audits, risk treatment, evidence collection, reporting, and integrations. Platforms that support continuous compliance keep the ISMS current between audits, and the best choice is generally the one your team will use every week, not the one with the longest feature list.
AI-native GRC for how teams work today.
How Scytale simplifies your ISMS
ISO 27001 work becomes harder when teams manage controls, evidence, and reviews in separate systems. Scytale‘s AI GRC platform brings ISMS workflows into one place, automating evidence collection, monitoring controls continuously, and using AI agents to review evidence and flag gaps so the ISMS stays current between audits. By using AI agents to review evidence, identify compliance gaps, and streamline remediation, Scytale helps teams spend less time on manual administration and more time strengthening security controls.
Scytale also maps controls across 80+ frameworks, including ISO 27001, SOC 2, GDPR, and SOX ITGC, so organizations reuse control work as their compliance program expands. Paired with a customizable Trust Center and dedicated GRC experts who support rollout, remediation, and audit preparation, Scytale helps organizations achieve and maintain ISO 27001 certification with less manual effort and continuous audit readiness.
FAQs about ISMS software
What is ISMS software?
ISMS software is a platform that helps organizations build, operate, and maintain an information security management system aligned with ISO 27001. It typically centralizes risk registers, Statement of Applicability records, policies, evidence, and internal audits in one system, replacing spreadsheets and shared folders.
Do you need ISMS software for ISO 27001 certification?
No, ISO 27001 does not require specific software, and organizations can achieve certification using documents and spreadsheets. However, ISMS software typically reduces manual effort, keeps evidence current, and makes surveillance and recertification audits easier to manage. Leading AI GRC platforms like Scytale automate evidence collection and control monitoring to shorten the path to certification.
What is the best ISMS tool for ISO 27001?
The best ISMS tool depends on company size, certification stage, and the frameworks the organization plans to add after ISO 27001. Purpose-built tools suit documentation-led programs, while automation platforms suit cloud-first teams. Scytale’s AI GRC platform is a strong fit for organizations that want ISMS automation, cross-framework mapping, and dedicated expert support in one system.
How much does ISMS software cost?
ISMS software pricing typically depends on company size, the number of frameworks, integrations, and whether services such as audit support are included. Most vendors provide custom quotes after a scoping conversation rather than publishing fixed prices, so organizations should compare total cost, including services and add-ons, before committing.
Can ISMS software manage other frameworks besides ISO 27001?
Yes, many ISMS software platforms support additional frameworks such as SOC 2, GDPR, HIPAA, and ISO 42001 alongside ISO 27001. Cross-framework mapping allows teams to reuse controls and evidence across standards instead of rebuilding the same work for each audit.
