


TL;DR: Cybersecurity tools in 2026
- Cybersecurity tools are essential for protecting SaaS organizations and maintaining compliance.
- These tools provide real-time monitoring and automated incident response, ensuring swift action against potential threats.
- When selecting cybersecurity tools, prioritize scalability, integration, expert support, and customization.
- Scytale stands out for its AI GRC platform, combining agentic workflows, continuous compliance monitoring, and expert guidance.
- The best cybersecurity tools improve cybersecurity management, reduce risks, and ensure business continuity.
Cybersecurity is no longer just a technical concern. With global cybercrime costs projected to hit $15.63 trillion annually by 2029, the financial impact of security failures is becoming impossible for businesses to ignore.
For SaaS organizations, this goes beyond security alone. Protecting sensitive data, ensuring system reliability, and meeting regulatory and industry requirements all depend on having the right cybersecurity tools in place. As IT environments become more complex, effective tools are essential for reducing risk, supporting overarching governance, risk, and compliance (GRC) goals, and maintaining operational continuity. In this article, we explain our evaluation criteria and cover the top cybersecurity tools that can help protect your organization in 2026.
Top 10 cybersecurity tools
- Scytale
- CrowdStrike Falcon
- Security Onion
- Wireshark
- SentinelOne
- Splunk
- Acunetix
- Burp Suite
- Tenable Nessus
- Metasploit
What are cybersecurity tools?
Cybersecurity tools are software solutions designed to protect an organization’s IT infrastructure, systems, networks, and sensitive data from cyber threats such as malware, ransomware, phishing, and data breaches.
These tools help organizations identify vulnerabilities, monitor suspicious activity, prevent unauthorized access, and detect and respond to potential security incidents. By addressing different areas of cybersecurity, they help businesses strengthen their security posture and protect the confidentiality, integrity, and availability of their data.
Cybersecurity tools cover a wide range of functions, including network security, endpoint protection, vulnerability scanning, penetration testing, and cyber threat intelligence. While some tools focus on preventing attacks, others help identify security weaknesses, investigate threats, or support incident response. Together, they provide multiple layers of protection, reduce security risks, and help organizations meet the requirements of relevant security and data privacy standards.
How we chose the best cybersecurity tools
The cybersecurity market includes hundreds of tools, and many overlap in the threats they claim to address. We reviewed tools across endpoint protection, network monitoring, SIEM, vulnerability scanning, penetration testing, and compliance automation, assessing each against common threats and the requirements of frameworks like SOC 2, ISO 27001, and GDPR. Here are the four criteria we used to narrow the list to the top 10:
Risk reduction
We prioritized tools that directly reduce exposure to real attacks by closing known attack vectors, such as unpatched systems, misconfigured networks, and vulnerable web applications. Strong data security controls across the endpoint, network, and application layers typically produce the clearest reduction in risk.
Compliance support
Security tools increasingly need to produce evidence, not just alerts. We assessed whether each tool supports audit readiness through logs, reports, and control evidence that map to framework requirements, favoring tools that support continuous compliance over point-in-time checks.
Integration effort
A tool that takes months to deploy or needs a dedicated specialist often delivers less value than its feature list suggests. We favored tools with native integrations across cloud infrastructure, identity providers, and existing security stacks, particularly for lean security teams.
Detection and response speed
The speed at which a team identifies and contains a threat often determines the size of the impact. We evaluated how quickly each tool surfaces meaningful alerts, filters noise, and supports automated response, favoring tools that shorten mean time to detect (MTTD) without overwhelming analysts.
Streamline GRC workflows with no blind spots.
Key benefits of cybersecurity tools for SaaS organizations
As cyber threats become more sophisticated, cybersecurity tools help SaaS businesses identify vulnerabilities, protect sensitive data, and respond to security incidents. From real-time threat detection to risk management and compliance support, these solutions strengthen security and reduce operational disruptions.
Here are the key benefits they offer:
- Prevents data breaches and cyberattacks: Protect sensitive data from unauthorized access and defend against AI-based cyberattacks.
- Compliance with industry regulations: Stay compliant with key security and regulatory frameworks such as GDPR, CCPA, and HIPAA to avoid costly penalties.
- Real-time, continuous monitoring of security risks: Continuously track your network, endpoints, and cloud environments for potential security vulnerabilities.
- Automated incident response and reporting: Streamline your response to threats, reducing the time to resolution and minimizing overall impact.
- Secure networks, endpoints, and cloud infrastructures: Provides comprehensive protection across all layers of your IT ecosystem, from on-premises systems to cloud environments.
10 best cybersecurity tools for 2026
Choosing the right cybersecurity tools is essential for protecting sensitive data, identifying vulnerabilities, and staying ahead of evolving cyber threats. With so many solutions available, finding the best fit depends on your organization’s security needs, infrastructure, and budget. Here are 10 of the best cybersecurity tools for 2026, covering a range of security functions and use cases.
1. Scytale
Scytale is a leading AI GRC platform that helps mid-market and enterprise SaaS businesses simplify security compliance, risk management, and audit readiness. Combining intelligent agentic workflows, continuous control monitoring, and expert guidance, Scytale helps organizations manage compliance across frameworks like SOC 2, ISO 27001, NIST CSF, and SOX ITGC.
The platform offers built-in penetration testing and advanced cybersecurity risk management, scaling with compliance programs to help businesses identify and address vulnerabilities, fortify security, and ensure resilience against emerging threats.
For example, after years of paying a Big Four firm for penetration tests, video platform SundaySky switched to Scytale and immediately had risks flagged that no prior test had caught, including exposure from existing customers.
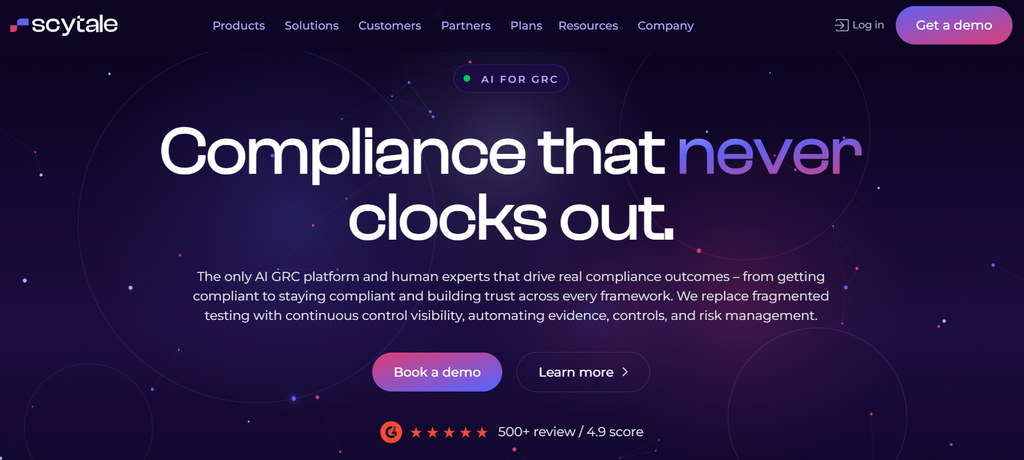
(Screenshot from Scytale’s website)
Why Scytale stands out:
- Continuous monitoring to identify security gaps, track risks, and maintain compliance.
- Agentic compliance that streamlines evidence collection, access reviews, and other manual compliance tasks
- Multi-framework management to reduce duplicate work across SOC 2, ISO 27001, GDPR, HIPAA, and more.
- Customizable Trust Center to showcase your security and compliance posture.
- Dedicated GRC experts offering guidance on security controls, risk management, and audit readiness.
- Seamless integrations with essential security and business tools for better visibility and efficiency.
2. CrowdStrike Falcon
CrowdStrike Falcon focuses on advanced endpoint protection and real-time threat intelligence, using machine learning and behavioral analytics to detect and prevent cyber threats. It offers comprehensive protection against malware, ransomware, and zero-day attacks.
(Screenshot from CrowdStrike Falcon’s website)
Key features:
- Endpoint protection with real-time intelligence against emerging threats
- Behavioral analytics to detect and prevent sophisticated cyberattacks
- Cloud-native architecture for centralized security across distributed environments
Limitations:
- Subscription costs may challenge businesses with limited budgets
- Advanced features may require dedicated security personnel
3. Security Onion
Security Onion is an open-source tool offering network security monitoring, intrusion detection, and security log analysis. It offers a customizable and affordable solution for businesses looking to build their security infrastructure from the ground up.
(Screenshot from Security Onion’s website)
Key features:
- Intrusion detection to identify suspicious network traffic patterns
- Full packet capture for detailed security incident investigations
- Integrates open-source tools for customizable network security monitoring
Limitations:
- Deployment requires technical knowledge of network security infrastructure
- Ongoing maintenance and tuning demand significant internal resources
4. Wireshark
Wireshark is a network protocol analyzer used for inspecting network traffic. It helps businesses identify vulnerabilities in network configurations and detect malicious activity in real-time.
(Screenshot from Wireshark’s website)
Key features:
- Real-time packet capture for detailed network traffic analysis
- Advanced filtering to isolate suspicious network activity quickly
- Open-source platform supporting extensive network protocols and analysis
Limitations:
- Packet analysis requires strong networking knowledge and experience
- Large traffic captures can consume significant system resources
5. SentinelOne
SentinelOne offers autonomous endpoint protection, providing real-time visibility and advanced incident response capabilities. It is designed to safeguard endpoints from modern cyber threats.
(Screenshot from SentinelOne’s website)
Key features:
- Autonomous endpoint protection with automated threat detection and remediation
- Behavioral ransomware detection to identify known and unknown attacks
- Flexible deployment options for cloud-connected and on-premises environments
Limitations:
- Advanced security packages may be costly for smaller businesses
- Automated responses require configuration to prevent operational disruptions
6. Splunk
Splunk is a powerful SIEM (Security Information and Event Management) tool that allows businesses to monitor, search, and analyze security data across their infrastructure. It helps improve security posture through real-time threat detection and response.
(Screenshot from Splunk’s website)
Key features:
- Centralized security monitoring across multiple systems and sources
- Advanced analytics to identify suspicious activity and anomalies
- Scalable cloud deployment for growing security data requirements
Limitations:
- Data ingestion and configuration require considerable implementation effort
- Licensing costs can increase with growing data volumes
7. Acunetix
Acunetix is an enterprise-grade web application vulnerability scanner that helps businesses detect and fix security vulnerabilities, such as SQL injection and XSS, across their applications.
(Screenshot from Acunetix’s website)
Key features:
- Automated vulnerability scanning across web applications and APIs
- Risk-based prioritization with actionable guidance for vulnerability remediation
Limitations:
- Primarily focused on web applications, excluding broader infrastructure
- Licensing may be expensive for businesses with fewer applications
8. Burp Suite
Burp Suite by PortSwigger is a popular tool for web application security testing, offering various features for penetration testing, vulnerability scanning, and manual testing.
(Screenshot from PortSwigger’s website)
Key features:
- Automated vulnerability scanning with detailed web security reports
- Manual testing for complex vulnerabilities, including XSS attacks
- Intercepting proxy to inspect and modify HTTP traffic
Limitations:
- Advanced testing requires specialized web application security expertise
- Professional editions may strain smaller security team budgets
9. Tenable Nessus
Tenable Nessus is a cybersecurity tool that helps businesses identify and assess risks in their IT infrastructure. It scans for a wide range of vulnerabilities, including missing patches and configuration errors, making it ideal for security assessments.
(Screenshot from Tenable Nessus’ website)
Key features:
- Vulnerability scanning to identify missing patches and misconfigurations
- Risk assessments with guidance for prioritizing security fixes
- Configurable scanning policies for different systems and networks
Limitations:
- Scan configuration can be challenging in complex environments
- Reporting interface may feel less intuitive for beginners
10. Metasploit
Metasploit is a penetration testing tool that simulates attacks to test the effectiveness of defenses. It includes an extensive exploit database and the ability to create custom exploits.
(Screenshot from Metasploit’s website)
Key features:
- Extensive exploit library for testing known security vulnerabilities
- Penetration testing to simulate attacks against vulnerable systems
- Manual and automated options for targeted security assessments
Limitations:
- Effective testing requires advanced penetration testing skills
- Aggressive exploit testing may disrupt vulnerable production systems
Overview of the top cybersecurity tools for 2026
| Cybersecurity tool | Best for |
| Scytale | Agentic GRC, continuous compliance monitoring, risk management, and penetration testing services |
| CrowdStrike Falcon | Endpoint protection & threat intelligence |
| Security Onion | Network security & intrusion detection |
| Wireshark | Packet analysis & network troubleshooting |
| SentinelOne | Autonomous endpoint protection |
| Splunk | SIEM (Security Information & Event Management) |
| Acunetix | Web application vulnerability testing |
| Burp Suite | Penetration testing & web app security |
| Tenable Nessus | Vulnerability scanning & risk assessment |
| Metasploit | Penetration testing & exploit development |
AI-native GRC for how enterprise teams work today.
Future-proof your cybersecurity strategy in 2026
Choosing the right cybersecurity tools is essential for protecting your business, managing security risks, and staying ahead of evolving threats. While different tools address different security needs, Scytale brings compliance, risk management, and continuous monitoring together in one AI GRC platform.
With intelligent agentic workflows, continuous security monitoring, and dedicated GRC experts, Scytale helps organizations identify compliance gaps, streamline risk assessments, reduce manual work, and maintain audit readiness across multiple frameworks. This helps businesses strengthen their security posture, simplify compliance management, and stay prepared as security risks and regulatory requirements evolve.
FAQs about top cybersecurity tools
Why is cybersecurity important?
Cybersecurity is crucial for protecting your business from data breaches, cyberattacks, and financial loss. It ensures the confidentiality, integrity, and availability of sensitive information, safeguarding it from unauthorized access, tampering, or destruction. As cyber threats continue to grow in sophistication, maintaining a strong cybersecurity strategy helps prevent costly downtime, preserve customer trust, and meet strict compliance requirements, ensuring your business remains secure and resilient.
How do I choose the right cybersecurity tool for my company?
To choose the right cybersecurity tool, assess your organization’s unique needs, such as endpoint protection, threat intelligence, compliance requirements, and scalability. Consider tools that offer real-time monitoring, automation, and expert support. Top cybersecurity platforms like Scytale can help streamline compliance processes and provide continuous monitoring, ensuring your cybersecurity efforts align with industry best practices.
What are the biggest cybersecurity threats in 2026?
In 2026, businesses face increasingly sophisticated cyber threats, including AI-powered cyberattacks, ransomware, phishing campaigns, and zero-day vulnerabilities. These threats are becoming more targeted and harder to detect, making it essential for SaaS businesses to stay ahead. Protecting against these risks requires advanced security tools that can detect and respond to threats in real time, helping organizations keep their systems and sensitive data secure.
What types of cybersecurity tools are available?
Cybersecurity tools encompass a wide range of solutions, including endpoint protection, network security tools, SIEM (Security Information and Event Management) platforms, penetration testing tools, and vulnerability scanners, among others. These tools are designed to help businesses monitor their systems, identify emerging threats, and maintain compliance with industry security standards. By using comprehensive cybersecurity platforms like Scytale, organizations can strengthen their defenses and respond more effectively to potential breaches.
Do cybersecurity tools guarantee complete protection?
No. While cybersecurity tools can significantly reduce the risk of breaches, no system is entirely immune to threats. However, these tools enhance an organization’s ability to detect, respond to, and recover from potential threats. By using leading cybersecurity tools like Scytale, businesses can minimize vulnerabilities, improve incident response times, and maintain a stronger security and compliance posture.
How much do cybersecurity tools cost?
Costs vary widely based on the type of tool, the size of the environment, and the level of support required. Open-source tools such as Wireshark and Security Onion are free but require in-house expertise, while commercial platforms are typically priced per endpoint, per asset, or by data volume. Organizations get the best return by mapping their highest risks and compliance obligations first, then investing in tools that address those gaps.
What is the best cybersecurity tool?
The best cybersecurity tool depends on an organization’s size, risk profile, and compliance requirements, since no single tool covers every layer of security. Tools like CrowdStrike Falcon focus on endpoint threats, while Tenable Nessus and Burp Suite specialize in vulnerability scanning and application testing. For SaaS organizations that need to connect security monitoring with compliance, Scytale’s AI GRC platform combines continuous monitoring, penetration testing, and multi-framework compliance in one place.
