
TL;DR: ISO 27001:2022 update
- ISO 27001:2022 is the latest version of the information security standard, with updated controls addressing modern security threats.
- The update reduces Annex A controls from 114 to 93, organized into four categories.
- Eleven new controls address threat intelligence, cloud security, data leakage prevention, and secure coding.
- Organizations certified under ISO 27001:2013 had until October 31, 2025, to transition. Previous certifications have since expired.
- Scytale’s AI GRC platform simplifies ISO 27001:2022 compliance through automated evidence collection, continuous monitoring, and dedicated GRC expert support.
Whether your organization is already ISO 27001 certified or preparing for certification, understanding the changes introduced in ISO 27001:2022 is essential for maintaining an effective information security management system (ISMS). While the core requirements of ISO 27001 remain largely unchanged, the update restructures Annex A controls to better address modern security risks and technologies.
From cloud security and threat intelligence to data protection and secure development, these changes affect how organizations implement and manage security controls. This article breaks down what changed in ISO 27001:2022, why it matters, and what organizations need to know to maintain compliance.
What is ISO 27001?
ISO 27001 is an internationally recognized standard for establishing, implementing, maintaining, and continually improving an information security management system (ISMS).
It provides a risk-based framework for protecting sensitive information, managing security threats, and demonstrating a commitment to information security. Organizations of all sizes can achieve ISO 27001 compliance to strengthen their security posture and build trust with customers and stakeholders. The key components of ISO 27001 include:
- Risk assessment and treatment: Identifying information security risks, evaluating their impact, and implementing appropriate controls to address them.
- Information security policies: Establishing documented policies that define security objectives, responsibilities, and requirements across the organization.
- Asset management: Identifying, classifying, and protecting information assets throughout their lifecycle.
- Access control: Restricting access to sensitive information and systems based on defined roles, responsibilities, and business needs.
- Incident management: Establishing processes to identify, report, respond to, and learn from information security incidents.
To achieve ISO 27001 certification, organizations must undergo an independent audit conducted by an accredited certification body. The initial certification audit consists of two main stages:
- Stage 1 audit: Reviews ISMS documentation, scope, and readiness for the certification assessment.
- Stage 2 audit: Evaluates whether the ISMS and its applicable security controls are effectively implemented and operating in practice.
Get ISO 27001 Compliant 90% Faster
Key updates: ISO 27001:2013 vs ISO 27001:2022
ISO 27001 is periodically updated to address evolving cybersecurity threats, emerging technologies, and changing business needs. The latest revision, ISO 27001:2022, introduces important changes to help organizations strengthen their information security management systems (ISMS) and maintain effective security practices.
The most significant changes involve the restructuring of Annex A, updated security controls, and clearer requirements for managing information security risks. While the core ISMS requirements remain largely unchanged, the revised standard better reflects modern security challenges, particularly around cloud technologies, data protection, and secure development. Here are the key changes introduced in ISO 27001:2022:
- Restructured controls: Annex A controls have been reduced from 114 to 93, consolidating overlapping measures while maintaining essential security coverage.
- Four control categories: Controls are now grouped into Organizational (37), People (8), Physical (14), and Technological (34) categories.
- 11 new security controls: New measures address emerging risks, including threat intelligence, cloud security, data leakage prevention, and secure coding.
- ISMS documentation updates: Organizations need to review their risk treatment plans, Statement of Applicability (SoA), and relevant security documentation to align with the revised controls.
What is new in the latest version of ISO 27001:2022?
ISO 27001:2022 introduces updates to address modern cybersecurity risks, strengthen information security, and simplify control management. Here are the key changes and what they mean for your organization.
Restructured Annex A controls
One of the biggest changes in ISO 27001:2022 is the reorganization of Annex A controls. The previous version included 114 controls across 14 domains, while the updated standard consolidates them into 93 controls across four categories: Organizational (37), People (8), Physical (14), and Technological (34).
This structure makes it easier to navigate security controls and identify relevant safeguards. Rather than removing essential protections, the update combines overlapping controls and reorganizes existing measures to reflect modern security practices.
New ISO 27001:2022 controls for emerging threats
ISO 27001:2022 introduces 11 new Annex A controls covering cloud security, threat intelligence, data protection, and secure development. These controls help organizations address modern cybersecurity risks and increasingly sophisticated cyberattacks. Here are the new controls and their purposes:
| Control number | Control | Purpose |
| 5.7 | Threat intelligence | Collect and analyze threat information to anticipate security threats. |
| 5.23 | Information security for use of cloud services | Manage security risks when selecting, using, and exiting cloud services. |
| 5.30 | ICT readiness for business continuity | Ensure critical ICT systems support recovery during disruptions. |
| 7.4 | Physical security monitoring | Monitor premises for unauthorized access and security incidents. |
| 8.9 | Configuration management | Maintain secure configurations across systems, software, and networks. |
| 8.10 | Information deletion | Securely delete information when no longer required. |
| 8.11 | Data masking | Protect sensitive information through masking techniques. |
| 8.12 | Data leakage prevention | Prevent unauthorized disclosure or transfer of sensitive information. |
| 8.16 | Monitoring activities | Detect unusual system activity and potential security incidents. |
| 8.23 | Web filtering | Restrict access to malicious or unsafe websites. |
| 8.28 | Secure coding | Apply secure coding practices to reduce software vulnerabilities. |
Increased focus on governance and technological controls
ISO 27001:2022 places greater emphasis on security governance and technological safeguards. Organizations should integrate information security into everyday business processes, from managing vendors to securing cloud infrastructure, while ensuring clear responsibilities and effective risk management.
Clearer ISO 27001:2022 requirements
The update refines several ISMS requirements without significantly changing the standard’s core structure. For example, Clause 6.3 introduces an explicit requirement to plan ISMS changes, while Clause 10 reorganizes requirements for continual improvement and corrective actions. Organizations should review these changes to keep their existing processes aligned with the standard.
Updates to documentation and evidence requirements
While core documentation requirements remain largely unchanged, organizations may need to update their compliance documentation to reflect revised controls. This includes reviewing the Statement of Applicability (SoA), risk treatment plans, and security policies to ensure they accurately reflect current practices and support audit readiness.
Addressing digital transformation challenges
ISO 27001:2022 addresses security challenges associated with cloud adoption and evolving digital technologies. Updated controls covering cloud security, configuration management, monitoring, and secure coding help organizations manage new risks and maintain effective security as their technology environments grow.

What does ISO 27001:2022 mean for your business?
The ISO 27001:2022 update affects how organizations assess security risks, implement controls, and maintain compliance. Whether you’re a growing startup pursuing certification or an established business maintaining an existing ISMS, understanding these changes helps ensure your security practices remain aligned with the current standard. Here is what the latest version of ISO 27001 means for your business:
- Protection against emerging threats: Strengthen security measures across cloud environments, supplier relationships, secure development, and incident detection to address evolving cybersecurity risks.
- Stronger risk management: Reassess your cybersecurity risks and ensure appropriate controls are in place to address threats relevant to your organization.
- Simplified control management: The reorganized Annex A structure makes it easier to navigate security controls and coordinate compliance efforts across different frameworks.
- New and updated security controls: Evaluate the 11 new controls and revised existing controls to identify gaps and determine which safeguards apply to your business.
- Updated compliance documentation: Review your Statement of Applicability (SoA), risk treatment plans, and security policies to ensure they reflect the revised controls and current practices.
- Leadership accountability: Ensure senior management continues to support the ISMS, allocate appropriate resources, and integrate information security into business decisions.
- Continuous improvement: Regularly monitor control effectiveness, review security risks, and update your ISMS as your organization and technology environment evolve.
- Risk-based flexibility: Select and implement security controls based on your organization’s specific risks, operational needs, and business environment.
- Updated certification requirements: Organizations certified under ISO 27001:2013 were required to transition by October 31, 2025. All new certifications must now meet ISO 27001:2022 requirements.
Why the ISO 27001:2022 update matters
For SaaS companies, the ISO 27001:2022 update helps ensure security practices keep pace with evolving technologies, cybersecurity threats, and business needs. The revised Annex A controls make it easier to manage security risks and align safeguards with business objectives, while new controls address critical areas such as cloud security, secure coding, threat intelligence, and data leakage prevention.
These changes are particularly important for businesses that rely on cloud infrastructure, handle sensitive customer data, or operate in rapidly changing digital environments. By aligning with ISO 27001:2022, organizations can strengthen their security posture, maintain an effective information security management system (ISMS), and demonstrate their commitment to protecting customer information. This also helps build trust with customers and partners while supporting long-term business growth.
How to implement ISO 27001:2022 for your business: Step-by-step guide
Implementing ISO 27001:2022 requires a structured approach to managing information security risks, establishing controls, and preparing for certification. Following a clear process helps organizations identify security gaps, meet the standard’s requirements, and maintain an effective information security management system (ISMS). Use this ISO 27001 checklist to guide your implementation:
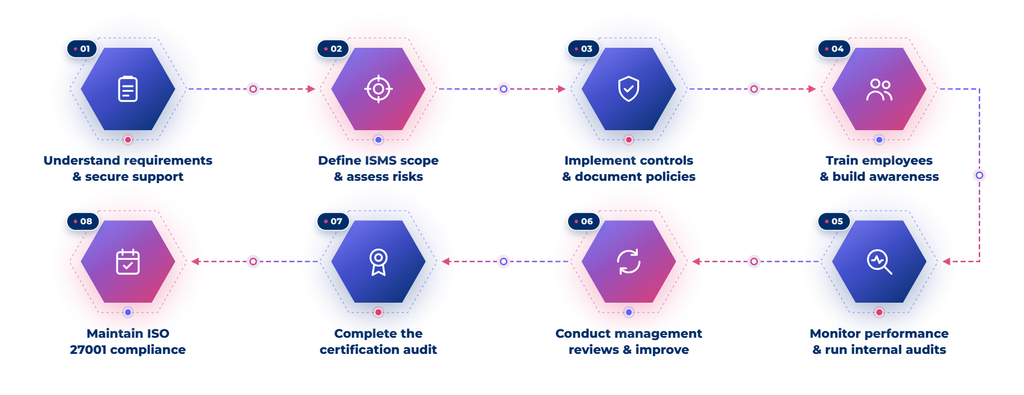
1. Understand the requirements and secure management support
Start by reviewing the ISO 27001:2022 requirements to understand what’s expected of your organization. Identify the key responsibilities, processes, and security measures needed to establish an effective ISMS. Secure leadership support early to ensure the necessary resources, budget, and responsibilities are in place.
2. Define your ISMS scope and assess risks
Determine which systems, processes, locations, and information assets your ISMS will cover. Conduct a risk assessment to identify potential security threats and evaluate their likelihood and impact on your organization. Use these findings to prioritize risks and determine where additional security measures are needed.
3. Implement security controls and document policies
Select and implement appropriate security controls based on your risk assessment, including relevant Annex A controls. Develop clear security policies and procedures that explain how your organization protects information and manages identified risks. Create a Statement of Applicability (SoA) to document which Annex A controls apply, justify inclusions and exclusions, and record their implementation status.
4. Train employees and build security awareness
Ensure employees understand their information security responsibilities and the policies relevant to their roles. Provide regular security awareness training to help teams recognize threats, follow procedures, and respond appropriately to potential incidents. Reinforce these practices through ongoing communication and training updates as security risks evolve.
5. Monitor performance and conduct internal audits
Regularly monitor your ISMS and evaluate whether security controls are operating effectively. Conduct internal audits at planned intervals to assess compliance with ISO 27001:2022 and identify gaps or weaknesses in your security practices. Document audit findings and address nonconformities through appropriate corrective actions to maintain audit readiness.
6. Conduct management reviews and improve your ISMS
Hold regular management reviews to evaluate ISMS performance, audit findings, security risks, and opportunities for improvement. Ensure leadership assesses whether the ISMS remains effective and aligned with organizational objectives. Use these insights to implement corrective actions, update security measures, and support continual improvement.
7. Prepare for and complete the certification audit
Once your ISMS is implemented and evaluated, select an accredited certification body and organize the documentation and evidence needed for the audit. The certification process includes a Stage 1 review of documentation and readiness, followed by a Stage 2 audit assessing how effectively your ISMS is implemented and operating. If successful, your organization receives ISO 27001:2022 certification and an ISO 27001 audit report.
8. Maintain ISO 27001 compliance
Certification is not a one-time activity, so continue monitoring controls, reviewing risks, and updating your ISMS as your business evolves. Conduct regular internal audits, management reviews, and corrective actions to identify weaknesses and maintain effective security practices. Annual surveillance audits and ongoing monitoring help support continuous compliance and keep your organization prepared for recertification.


Streamline ISO 27001:2022 compliance with Scytale
Scytale‘s AI GRC platform helps organizations implement and maintain ISO 27001:2022 through automated evidence collection, continuous control monitoring, and centralized audit management. The platform flags control gaps as they appear and keeps documentation ready for certification and surveillance audits, reducing the manual effort involved in running an ISMS.
Scytale also supports multi-framework compliance by mapping ISO 27001 controls to frameworks such as SOC 2, ISO 42001, GDPR, HIPAA, and SOX ITGC to reduce duplicate work. Combined with a customizable Trust Center and dedicated GRC experts, Scytale helps organizations stay compliant year-round and demonstrate a strong security posture to customers and auditors.
FAQs about ISO 27001:2022 update
How do the new controls in ISO 27001:2022 improve security measures?
The 11 new Annex A controls address modern cybersecurity risks, including cloud security, threat intelligence, data leakage prevention, and secure coding. They help organizations strengthen protection, identify potential threats earlier, and maintain effective security measures as technology evolves.
Why was ISO 27001 updated from 2013 to 2022, and what does it mean for my business?
ISO 27001 was updated to reflect changes in technology, cybersecurity threats, and business practices since 2013. For your organization, this means reviewing existing controls, addressing security gaps, and updating your information security management system (ISMS) to align with the latest requirements.
When did organizations need to fully transition to ISO 27001:2022?
Organizations certified under ISO 27001:2013 had until October 31, 2025, to transition to ISO 27001:2022. Certificates issued under the 2013 version are no longer valid, and all certification, surveillance, and recertification audits must now follow the updated standard.
How long is an ISO 27001 certificate valid?
An ISO 27001 certificate is typically valid for three years, provided the organization maintains compliance. Surveillance audits generally take place annually, with a recertification audit required before the certificate expires. If certification lapses, additional assessments may be needed to regain certified status.
What is the difference between ISO 27001 and SOC 2?
ISO 27001 is an international information security standard that leads to certification by an accredited certification body. SOC 2 is an AICPA attestation framework that results in an independent CPA’s report evaluating controls against the Trust Services Criteria. Both share similar security requirements, allowing platforms like Scytale to map controls and reuse evidence across frameworks to reduce duplicate compliance work.
How do ISO 27001 and ISO 42001 overlap?
Both standards follow a similar management system structure, with shared requirements for risk management, leadership, internal audits, and continual improvement. While ISO 27001 focuses on information security, ISO 42001 addresses AI governance and risk management. Organizations implementing both can reuse relevant policies, processes, and evidence, while Scytale’s AI GRC platform helps map shared controls and simplify compliance management.
