
TL;DR: Scytale vs Thoropass vs Vanta
- Managing SOC 2 and ISO 27001 together is easier when shared controls and evidence can be reused across both frameworks.
- Compliance platforms help reduce manual work by automating evidence collection, monitoring controls, and streamlining audit preparation.
- When comparing platforms, consider automation capabilities, multi-framework support, expert guidance, auditor flexibility, and total compliance costs.
- The right platform depends on your organization’s size, internal resources, compliance requirements, and future growth plans.
- Scytale’s AI GRC platform combines automation, continuous monitoring, and dedicated GRC experts to simplify compliance across multiple frameworks.
Managing SOC 2 and ISO 27001 together can quickly become complicated, especially when teams handle controls, evidence collection, and audit preparation separately. Without the right tools, this often leads to duplicated work, increased manual effort, and added pressure on internal resources. A compliance platform that supports both frameworks can help streamline these processes and maintain audit readiness.
When comparing Scytale vs Thoropass vs Vanta, it’s important to look beyond automation alone. Each platform takes a different approach to multi-framework management, audit support, and expert guidance. In this article, we compare their key features, pricing, and audit models to help you choose the right platform for your organization’s compliance needs.
Scytale vs Thoropass vs Vanta at a glance
Scytale, Thoropass, and Vanta all help automate SOC 2 and ISO 27001 compliance, but each takes a different approach to managing multiple frameworks, supporting audits, and guiding compliance teams. Understanding these differences can help organizations find a solution that fits their internal resources, simplifies day-to-day compliance tasks, and supports their long-term goals.
Scytale
Scytale is an AI GRC platform that combines intelligent automation, continuous monitoring, and dedicated GRC experts to simplify compliance across multiple frameworks. It automates evidence collection, maps shared controls across SOC 2 and ISO 27001, and helps teams maintain audit readiness with less manual work. Organizations also benefit from expert guidance throughout the compliance process and the flexibility to choose their own independent auditor.
Thoropass
Thoropass combines compliance automation software with in-house audit services, allowing organizations to manage readiness and audits through one provider. Its platform supports control mapping, evidence collection, and audit preparation across SOC 2 and ISO 27001. This approach is particularly suited to smaller teams looking for a more consolidated compliance and audit process.
Vanta
Vanta focuses on compliance automation through a broad integration library, automated evidence collection, and continuous control monitoring. It supports SOC 2 and ISO 27001 with shared controls and evidence across frameworks, while audits are conducted through external audit partners. Vanta is generally suited to organizations with dedicated internal compliance resources that prefer managing their programs independently.
Platform comparison summary
| Platform | Best for | Key strength | Audit model |
|---|---|---|---|
| Scytale | Startups to enterprises managing multiple frameworks | AI GRC automation, continuous monitoring, and dedicated GRC experts | Independent auditor of your choice, with expert-guided readiness |
| Thoropass | Lean teams wanting one vendor | Built-in audit | In-house audit arm |
| Vanta | Teams with strong internal ownership | Broad integrations | Partner auditor network |
Running SOC 2 and ISO 27001 together: What to look for
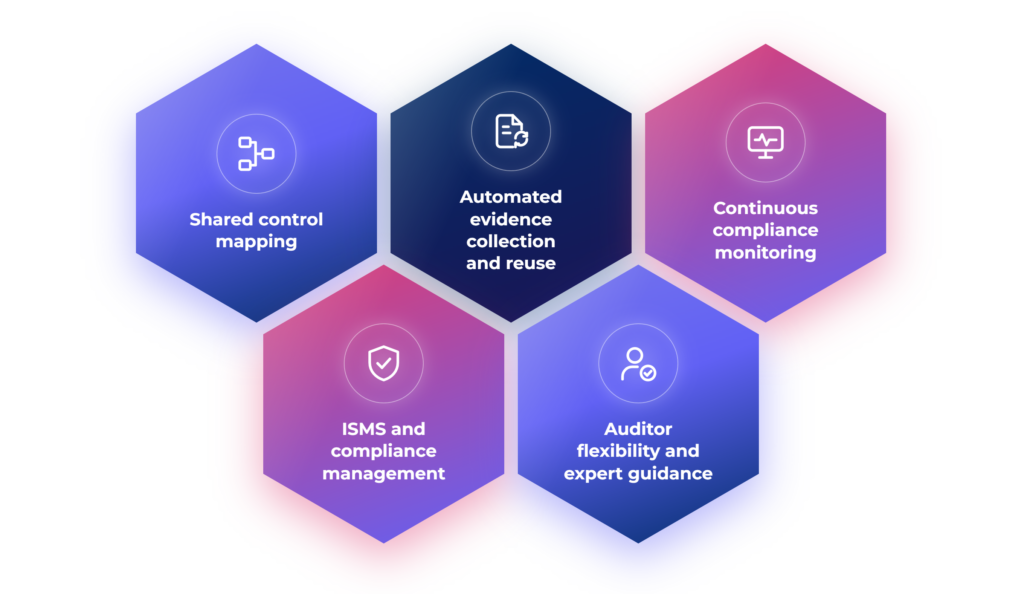
SOC 2 and ISO 27001 share many security requirements, including access management, risk assessments, vendor oversight, and incident response. However, each framework has its own audit and documentation requirements. Choosing a platform that supports both can help reduce duplicate work, simplify compliance management, and keep teams audit-ready. Here are the key capabilities to look for:
Shared control mapping
Effective SOC 2 compliance software should allow organizations to manage shared controls across both SOC 2 and ISO 27001 without duplicating work. For example, access reviews, vendor assessments, and security policies can support requirements in both frameworks. Automated control mapping helps teams manage these requirements in one place, reducing repetitive tasks and making it easier to track compliance across frameworks.
Automated evidence collection and reuse
Collecting evidence separately for each framework can take up significant time and resources. Look for a platform that automatically collects evidence from cloud systems, identity providers, HR tools, and other connected applications. Evidence should be reusable across SOC 2 and ISO 27001 wherever requirements overlap, reducing manual effort and helping teams maintain SOC 2 compliance while keeping documentation up to date for ISO 27001 audits.
Continuous compliance monitoring
Compliance shouldn’t be limited to preparing for an annual audit. Continuous monitoring helps organizations track control performance, identify gaps, and address issues before they become audit findings. A platform that provides ongoing visibility into compliance status can help teams maintain security controls throughout the year, rather than relying on last-minute evidence collection and manual reviews.
ISMS and compliance management
Unlike SOC 2, ISO 27001 requires organizations to establish and maintain an information security management system (ISMS). This includes risk assessments, internal audits, management reviews, and a Statement of Applicability. Effective ISO 27001 software should support these activities alongside SOC 2 requirements, helping teams manage policies, risks, documentation, and compliance responsibilities in one centralized system.
Auditor flexibility and expert guidance
SOC 2 reports must be issued by licensed CPA firms, while accredited certification bodies issue accredited ISO 27001 certifications. When evaluating platforms, consider whether you can choose your preferred auditors and how easily they can access the necessary evidence. Dedicated compliance experts can also help with framework scoping, documentation, remediation, and audit preparation, reducing the burden on internal teams managing both frameworks.
Streamline GRC workflows with no blind spots.
How each platform handles SOC 2 and ISO 27001
Managing SOC 2 and ISO 27001 together requires a platform that can map shared controls, automate evidence collection, and support both audit processes without duplicating work. A strong multi-framework compliance platform helps teams manage overlapping requirements in one place while keeping track of each framework’s specific needs. Here’s how Scytale, Thoropass, and Vanta approach multi-framework compliance.
Scytale
Scytale’s AI GRC platform helps organizations manage SOC 2 and ISO 27001 through automated control mapping, evidence collection, and continuous monitoring. Shared controls are mapped across both frameworks, allowing teams to collect evidence once and reuse it wherever requirements overlap. This reduces duplicate work and makes it easier to manage compliance across multiple frameworks from one centralized platform.
Scytale also uses AI agents to review evidence, identify compliance gaps, and streamline ongoing tasks. Dedicated GRC experts support teams with framework requirements, documentation, and audit preparation, while organizations retain the flexibility to work with their preferred independent auditors.
Thoropass
Thoropass combines compliance automation with in-house audit services, helping organizations manage SOC 2 and ISO 27001 through a single provider. Its platform supports cross-framework control mapping, allowing teams to reuse shared evidence and documentation across both frameworks rather than managing separate compliance processes.
Because Thoropass provides both readiness support and audit services, evidence collection and audit preparation can be coordinated within the same system. This approach can simplify communication between compliance teams and auditors, particularly for organizations looking to manage multiple audits through one provider.
Vanta
Vanta supports SOC 2 and ISO 27001 through automated evidence collection, continuous control monitoring, and cross-framework control mapping. Its integration library connects with cloud services, identity providers, HR platforms, and other business tools to collect evidence that can be reused across overlapping framework requirements.
Organizations can manage shared controls and track compliance progress through Vanta’s centralized platform, reducing the need to collect the same evidence separately for each audit. When evaluating Vanta alternatives, teams should also consider auditor flexibility and support. Vanta works with external audit partners, allowing organizations to select an auditor while managing compliance readiness through the platform.
AI-native GRC for how teams work today.
Built-in audits vs auditor networks
The audit model you choose can affect compliance timelines, costs, and how much work falls on your internal team. Some platforms offer built-in audit services, while others let you work with independent auditors. Here’s how these approaches compare and what to consider when managing SOC 2 and ISO 27001 together.
The case for built-in audits
Thoropass combines compliance readiness and audit services under one provider, helping reduce handoffs between teams and auditors. Its in-house auditors can work closely with the compliance process, potentially speeding up evidence reviews and reducing last-minute issues. This approach is particularly useful for smaller teams looking to simplify audit preparation and manage both frameworks through one provider.
The case for independent auditor choice
Vanta works with a network of external audit partners, allowing organizations to select an auditor and arrange audit services separately. This gives teams more flexibility, particularly if they already have an established auditor relationship or specific audit requirements. However, managing separate software and audit providers can involve additional coordination, contracts, and timelines.
A guided middle path
Scytale combines independent auditor choice with dedicated GRC expert support. Its experts guide teams through compliance readiness, evidence reviews, and audit preparation while helping coordinate the audit process. This allows organizations to work with their preferred auditors while reducing the time and effort required from internal teams.
Pricing compared
Pricing for SOC 2 and ISO 27001 compliance platforms varies depending on company size, the number of frameworks, and the level of automation and support required. Scytale, Thoropass, and Vanta offer different pricing structures, making it important to understand what’s included in each subscription and which services cost extra.
When comparing costs, consider more than just the software subscription. Additional frameworks, audit fees, expert support, and internal resources can all affect the total cost of compliance. Here’s how the three platforms compare based on publicly available pricing information:
| Platform | Pricing model | Public starting price | Audit fees |
| Scytale | Tailored pricing based on frameworks, automation needs, and dedicated GRC support | Not publicly listed; custom quote required | Separate; third-party audit services available |
| Thoropass | Quote-based, with separate software and audit subscriptions | From $8,700/year for the platform and one framework | In-house SOC 2 audits from $5,800/year |
| Vanta | Quote-based; Essentials, Plus, Professional, and Enterprise plans | No public starting price; custom quote required | Separate; pricing depends on the independent auditor and audit scope |
Which is right for you?
Choosing the right compliance platform depends on your organization’s size, internal resources, and long-term compliance goals. Whether you’re managing SOC 2 and ISO 27001 for the first time or expanding into additional frameworks, it’s important to consider the level of automation, expert support, audit flexibility, and continuous compliance capabilities each platform offers.
One vendor for software and audit
Choose Thoropass if you want to manage compliance readiness and audits through a single provider. Its combined software and in-house audit services can simplify coordination and reduce the need to work with multiple vendors. This approach is particularly suitable for smaller teams with limited internal compliance resources.
Automation with internal compliance ownership
Choose Vanta if your organization has a dedicated compliance team and prefers managing its program internally. Its broad integration library, automated evidence collection, and continuous monitoring capabilities help streamline compliance tasks, while external audit partners provide flexibility when selecting an auditor.
AI GRC automation with dedicated expert support
Choose Scytale if your organization needs a comprehensive AI GRC platform that combines intelligent automation with dedicated GRC expert support. Built for startups, growing businesses, and enterprises, Scytale helps teams simplify complex compliance processes, reduce manual effort, and manage multiple frameworks efficiently, while maintaining the flexibility to work with their preferred independent auditors.


Why teams choose Scytale for SOC 2 and ISO 27001
Managing SOC 2 and ISO 27001 together requires more than meeting individual framework requirements. Teams need clear ownership, consistent documentation, and a reliable way to track compliance progress without adding unnecessary work. Scytale helps organizations build a more structured and efficient compliance program, making it easier to coordinate responsibilities, address gaps, and keep everyone aligned throughout the compliance process.
Rather than treating compliance as a series of separate audit projects, Scytale helps teams take a more proactive approach. With ongoing visibility into control performance and continuous compliance, organizations can identify issues earlier, make informed decisions, and stay prepared as requirements evolve. This helps reduce last-minute audit pressure and makes compliance easier to manage as the business grows.
FAQs about Scytale vs Thoropass vs Vanta
What are the main differences between Scytale, Thoropass, and Vanta for SOC 2 and ISO 27001?
The main differences sit in audit model, support depth, and cross-framework workflow design. Scytale combines AI-driven automation with dedicated guidance and independent auditor flexibility. Thoropass centers more on bundled audit coordination. Vanta focuses on software-led automation with a partner-based auditor ecosystem for teams managing more of the process internally.
Which platform is best for achieving SOC 2 and ISO 27001 compliance?
The best platform is the one that matches how your team intends to run the program. Scytale’s AI GRC platform fits teams that want one control set across both frameworks plus expert guidance, Thoropass fits buyers who prefer a bundled audit, and Vanta fits teams with the internal capacity to manage the workflow themselves.
How does the pricing of Scytale compare with Thoropass and Vanta?
All three platforms offer customized pricing based on compliance requirements, frameworks, and services. Scytale provides tailored pricing based on automation needs and dedicated GRC support, while Thoropass publishes starting prices for its platform and in-house audit services. Vanta offers quote-based pricing across its subscription plans. When comparing costs, consider software, audit fees, and expert support to understand the total investment.
Which platform is best for startups and growing businesses?
The best platform for a startup is the one that matches its internal compliance capacity. Leading AI GRC platforms like Scytale suit teams without a dedicated compliance hire because experts guide the process, while Vanta suits startups with strong internal ownership and Thoropass suits teams that want fewer vendors during early audit cycles.
