

TL;DR: SOC 2 compliance software
- SOC 2 compliance software simplifies the process of achieving and maintaining compliance while reducing manual work.
- Automation streamlines time-consuming tasks such as evidence collection, control monitoring, risk assessments, and audit preparation.
- Continuous monitoring helps teams identify compliance gaps earlier and stay prepared for audits throughout the year.
- The right platform should fit your organization’s current needs while supporting future compliance requirements and growth.
- Scytale stands out as a leading SOC 2 compliance platform, combining AI-powered automation, multi-framework management, continuous monitoring, and dedicated GRC expert support.
SOC 2 has become an important way for organizations to demonstrate that they take security and customer data protection seriously. With growing customer expectations, choosing the right software can make the process easier to manage at every stage.
There are many SOC 2 platforms available, each offering different capabilities and levels of support. In this article, we compare the best SOC 2 compliance software for 2026 and what to consider when choosing the right solution.
Best SOC 2 compliance software
- Scytale
- Optro
- Apptega
- LogicGate
- OneTrust
- Qualys
- Secureframe
What is SOC 2 compliance software?
SOC 2 compliance software is a platform that helps organizations automate, manage, and maintain the processes required for SOC 2 compliance.
Managing SOC 2 manually can quickly become time-consuming as teams collect evidence, update policies, assess risks, monitor controls, and prepare for SOC 2 audits. SOC 2 compliance software brings these activities into one place and automates repetitive tasks, helping teams reduce manual work, improve visibility, and identify gaps earlier.
These tools can support startups working toward their first SOC 2 report as well as larger organizations scaling their compliance program. More advanced platforms may also combine automation with expert guidance, helping teams understand requirements, implement the right controls, and maintain audit readiness as their compliance program grows.
Why your business needs SOC 2 compliance software in 2026
As SOC 2 becomes an important requirement for more businesses, managing compliance manually can consume significant time and make it harder to maintain visibility between audits. SOC 2 compliance automation software helps organizations build a more efficient and sustainable approach to compliance. Here are the main reasons businesses need SOC 2 compliance software:
Reduce manual compliance work
SOC 2 requires teams to manage recurring activities across evidence collection, controls, policies, risk assessments, and audit preparation. Automating these processes reduces repetitive administrative work, improves consistency, and gives security and compliance teams more time to focus on resolving issues and strengthening their overall security program.
Maintain SOC 2 compliance between audits
SOC 2 compliance requires ongoing attention after the initial audit is complete. Continuous monitoring helps teams track control performance, identify gaps or failed controls earlier, and keep evidence current throughout the year, reducing the last-minute work required when the next assessment approaches.
Improve ownership and visibility
SOC 2 responsibilities often extend across security, IT, HR, engineering, and leadership, making clear ownership important. Centralizing compliance activities gives teams one place to assign responsibilities, monitor outstanding tasks, track remediation, and understand the overall status of the SOC 2 program.
Support compliance as the business grows
Compliance requirements can become more complex as organizations grow, serve larger customers, and take on additional security or privacy requirements. SOC 2 software provides a scalable foundation that helps teams manage increasing controls, evidence, users, and frameworks without relying on more spreadsheets or disconnected processes.
Get SOC 2 Compliant 90% Faster
Key features to look for in SOC 2 compliance software
Beyond usability and integrations, the strongest SOC 2 platforms should provide capabilities that help teams manage controls, documentation, risk, and audit requirements throughout the compliance lifecycle. Here are the key features to look for:
Automated evidence collection
Automated evidence collection pulls required documentation and compliance data directly from connected systems. This creates a more reliable evidence trail, reduces the risk of missing or outdated records, and makes it easier to demonstrate that controls are operating as expected.
Continuous control monitoring
Continuous control monitoring helps teams verify that controls remain effective between assessments. When a control fails or falls out of compliance, teams can identify the issue earlier and take corrective action before it becomes an audit finding.
Policy management
Policy management provides a structured way to create, approve, distribute, and maintain security and compliance policies. Centralizing policies also makes it easier to track ownership, manage updates, and demonstrate that required policies are current and communicated across the organization.
Risk assessment and management
Risk management capabilities help teams identify, assess, prioritize, and track risks that could affect their SOC 2 environment. The platform should make it easier to connect identified risks with relevant controls and monitor remediation, particularly across the applicable Trust Services Criteria.
Audit management
Strong SOC 2 software should help teams organize evidence, controls, findings, and auditor requests in one place. Audit management capabilities create a clearer workflow between the organization and its auditor, making it easier to track outstanding requests and move through the assessment efficiently.
Key SOC 2 compliance software features
| Feature | What it does | Why it matters |
| Automated evidence collection | Collects evidence directly from connected systems | Reduces manual work and improves evidence accuracy |
| Continuous control monitoring | Tracks control performance and identifies gaps | Helps teams address issues before audits |
| Policy management | Centralizes policy creation, approvals, and updates | Keeps policies current and consistently managed |
| Risk management | Identifies, assesses, and tracks risks | Helps prioritize risks and monitor remediation |
| Audit management | Organizes evidence, findings, and auditor requests | Creates a smoother, more efficient audit process |
Best SOC 2 compliance software in 2026
Choosing SOC 2 compliance software can make the compliance process easier to manage and give teams greater visibility as requirements evolve. The right solution will depend on your organization’s needs, resources, and approach to compliance. Here are the best SOC 2 compliance software platforms for 2026:
1. Scytale
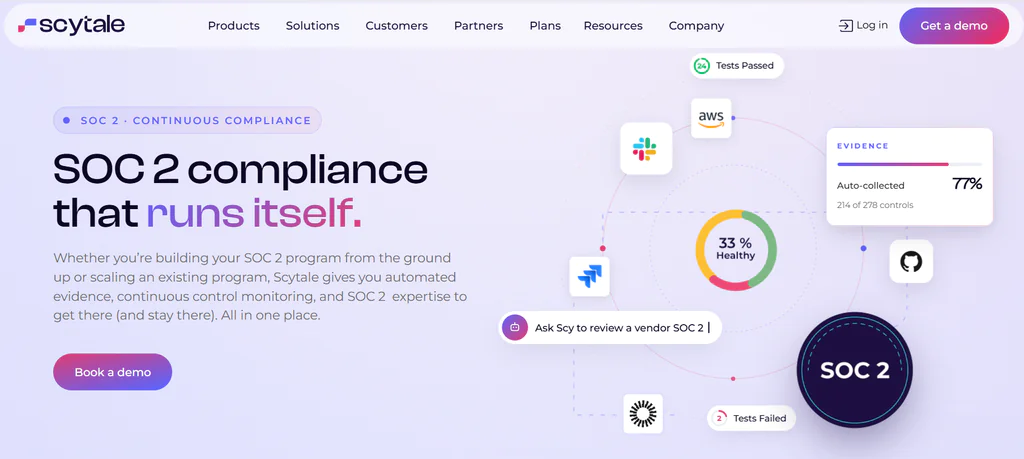
Scytale stands out as the best SOC 2 compliance software for 2026, offering an AI-powered platform that simplifies achieving and maintaining SOC 2 compliance. Built for growing companies and enterprises, Scytale connects controls, evidence, policies, risks, and system data, giving teams clear visibility across their SOC 2 program.
Scytale’s multi-agent GRC suite reviews evidence, validates compliance activities, and identifies areas that need attention. With 100+ integrations and multi-framework cross-mapping, teams can manage SOC 2 alongside ISO 27001, HIPAA, GDPR, SOX ITGC, and other requirements while reducing duplicate work.
(Screenshot from Scytale’s website)
Why Scytale is the best:
- Centralized SOC 2 management brings controls, evidence, policies, risks, and audit activities together in one platform.
- AI-powered automation that reduces manual SOC 2 work across evidence collection, control monitoring, access reviews, and gap detection.
- Continuous control monitoring that helps teams identify failed controls and address compliance gaps before the SOC 2 audit.
- Multi-framework cross-mapping that lets teams reuse SOC 2 controls and evidence across ISO 27001, HIPAA, GDPR, and other requirements.
- Dedicated GRC expert support that provides hands-on guidance with SOC 2 requirements, control implementation, evidence, and audit preparation.
- Customizable Trust Center that helps teams share their SOC 2 and security posture with customers and prospects.
2. Optro
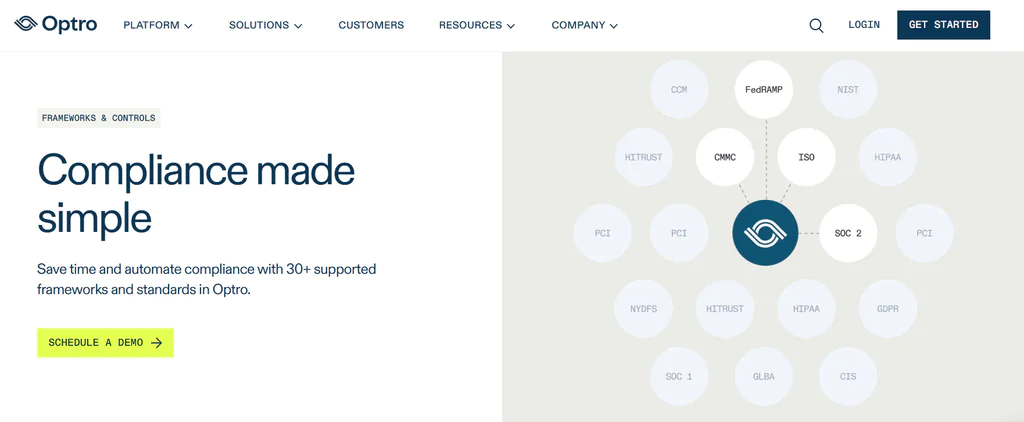
Optro is a compliance management platform that helps organizations structure and oversee security and compliance activities. Its straightforward approach can suit teams looking to organize compliance workflows and gain clearer visibility into their progress.
(Screenshot from Optro’s website)
Key strengths
- Centralized dashboards provide clear visibility into compliance progress, outstanding requirements, and activities requiring attention across different programs.
- Structured workflows help teams coordinate recurring compliance activities, assign responsibilities, and maintain consistent processes across the organization.
- Risk management capabilities help teams connect compliance requirements with relevant security risks and prioritize areas requiring further attention.
- Accessible workflows make ongoing compliance responsibilities easier to organize, track, and manage across different teams and stakeholders.
Limitations
- Organizations with highly specialized compliance programs may need additional customization to accommodate unique processes and specific internal requirements.
- Teams should confirm that available integrations provide sufficient coverage for the systems and evidence sources within their environment.
- Organizations requiring hands-on compliance guidance should evaluate whether the available expert support meets their SOC 2 program needs.
3. Apptega
Apptega is a cybersecurity compliance management platform that supports SOC 2 alongside a broader range of security frameworks. It is particularly relevant for organizations and service providers that need to structure and manage multiple security compliance programs.
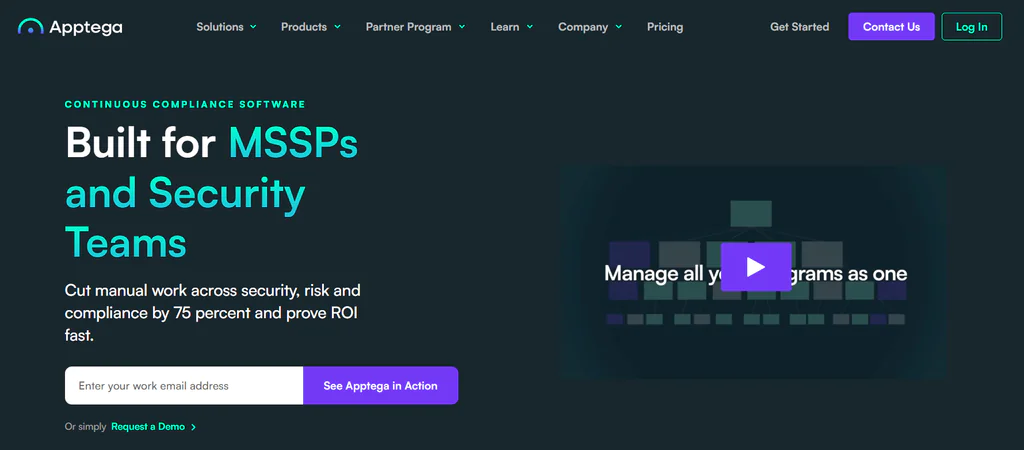
(Screenshot from Apptega’s website)
Key strengths
- Framework crosswalking helps teams identify overlapping controls, reuse existing work, and manage SOC 2 alongside other security standards.
- Multi-tenant architecture enables MSPs and MSSPs to manage separate compliance programs for multiple clients from one environment.
- Centralized dashboards provide visibility and reporting across frameworks, assessments, controls, findings, and other ongoing compliance activities.
- AI-assisted recommendations help teams interpret security requirements, understand potential gaps, and determine appropriate actions across compliance programs.
Limitations
- Complex environments may require additional upfront planning and configuration before teams can fully establish their compliance programs.
- Organizations should confirm available integrations support the specific systems and evidence sources required for their SOC 2 scope.
- Broader cybersecurity capabilities may provide more functionality than organizations focused primarily on straightforward SOC 2 compliance actually need.
4. LogicGate
LogicGate supports SOC 2 compliance through its broader Risk Cloud GRC platform, connecting compliance with enterprise risk management. Its configurable approach is particularly suited to mature organizations that want to adapt compliance processes around established internal workflows.
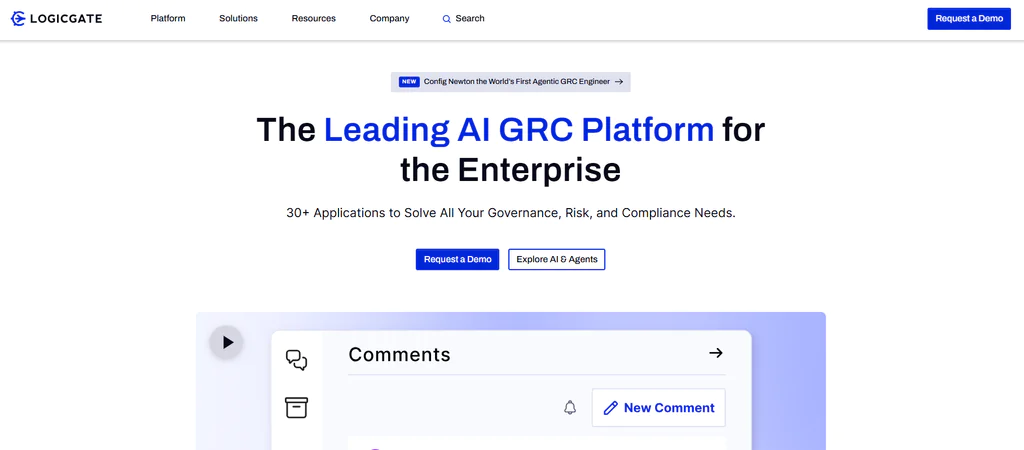
(Screenshot from LogicGate’s website)
Key strengths
- Configurable applications allow organizations to tailor SOC 2 controls, assessments, approvals, and workflows around their established internal processes.
- Built-in crosswalks identify overlapping requirements between SOC 2 and other standards, helping teams coordinate multiple compliance programs.
- Risk management capabilities connect compliance findings with broader operational and enterprise risks, providing additional context for decision-making.
- Custom implementations give mature organizations greater flexibility when building specialized workflows for complex or highly specific compliance requirements.
Limitations
- Extensive configurability can require additional upfront planning and internal resources before organizations establish their preferred SOC 2 workflows.
- Smaller compliance teams focused primarily on SOC 2 may not need the platform’s broader enterprise risk management functionality.
- Organizations seeking a more guided SOC 2 journey may prefer software with more predefined workflows and implementation processes.
5. OneTrust
OneTrust supports SOC 2 within a broader platform spanning security, risk, privacy, and data governance. It can be particularly relevant for larger organizations that want their SOC 2 program connected with wider privacy and data management requirements.
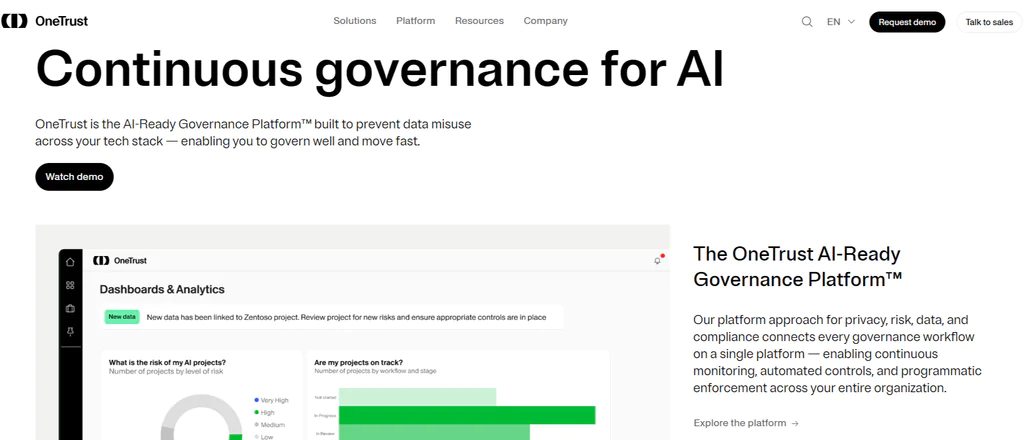
(Screenshot from OneTrust’s website)
Key strengths
- Scoping capabilities help organizations determine which SOC 2 policies, controls, and requirements apply to their specific compliance environment.
- Risk assessment functionality helps teams connect identified risks and supporting evidence with relevant controls and internal compliance requirements.
- Auditor collaboration capabilities provide a structured environment for managing documentation, requests, and communication throughout the SOC 2 assessment.
- Privacy and data governance capabilities complement SOC 2 for organizations managing significant regulatory and data protection responsibilities.
Limitations
- The platform’s broad scope may provide more functionality than organizations focused primarily on SOC 2 compliance actually require.
- New users may face a steeper learning curve when navigating its extensive range of privacy, risk, and compliance capabilities.
- Smaller organizations with straightforward requirements may prefer a more focused platform centered specifically on security compliance automation.
6. Qualys
Qualys takes a more technical approach to SOC 2 through its cloud-based security and compliance capabilities. It is particularly relevant for enterprises that want asset, vulnerability, configuration, and policy compliance data closely connected with their security program.
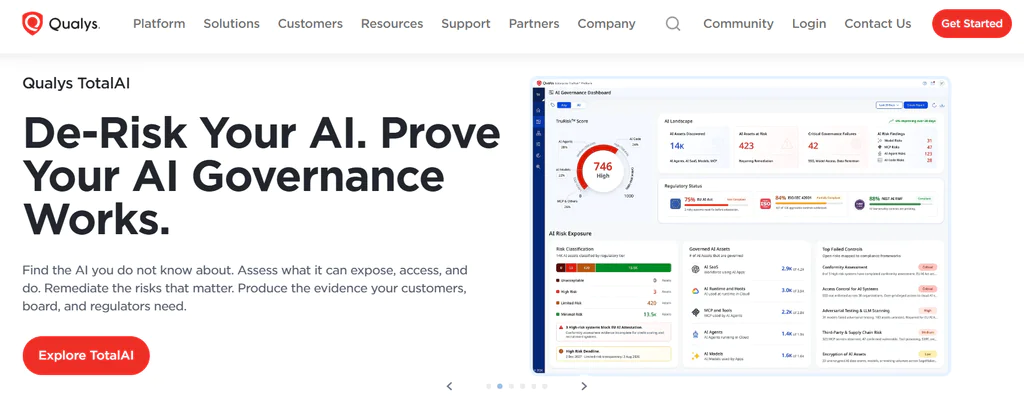
(Screenshot from Qualys’ website)
Key strengths
- Asset discovery provides security teams with visibility across complex cloud, on-premise, endpoint, and hybrid environments within compliance scope.
- Configuration assessments evaluate systems against established security policies, helping technical teams identify weaknesses and potential compliance gaps.
- Technical control evidence can be collected directly from enterprise assets to support ongoing compliance validation and assessment activities.
- Compliance dashboards help teams identify configuration drift, prioritize remediation activities, and monitor technical security requirements more effectively.
Limitations
- Qualys is less focused on managing the complete SOC 2 lifecycle than dedicated end-to-end compliance automation platforms.
- Extensive technical security functionality may introduce unnecessary complexity for smaller teams primarily focused on managing SOC 2 requirements.
- Non-technical stakeholders may require additional processes for managing policies, organizational controls, and broader SOC 2 governance activities.
7. Secureframe
Secureframe is a security compliance automation platform designed to help organizations achieve and maintain SOC 2 and other security frameworks. It provides a structured environment for managing controls, workforce requirements, vendors, cloud security, and audit preparation.
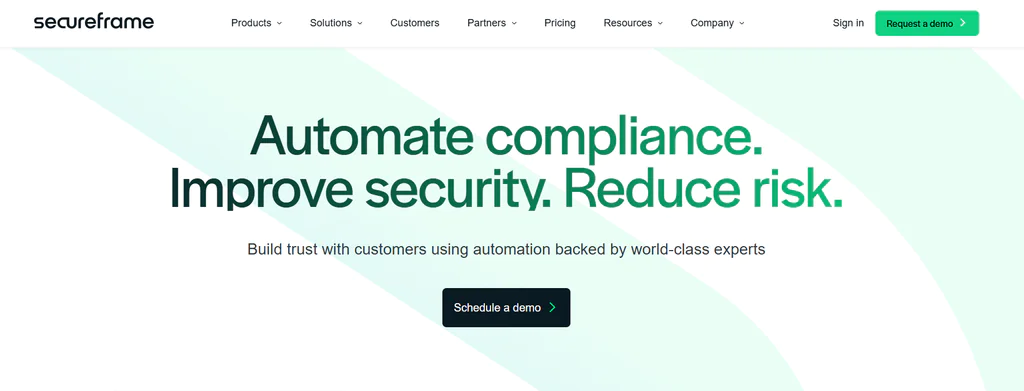
(Screenshot from Secureframe’s website)
Key strengths
- Cloud infrastructure scanning helps teams identify security configuration issues and technical weaknesses that could affect SOC 2 compliance.
- Employee workflows support onboarding, training, access management, and other workforce requirements relevant to maintaining SOC 2 compliance.
- Vendor management capabilities help teams assess third-party security risks and incorporate supplier oversight into their broader compliance program.
- Readiness assessments provide a structured way to evaluate compliance status and identify remaining gaps before beginning the formal audit.
Limitations
- Custom controls may require additional manual configuration or evidence collection depending on the complexity of the organization’s environment.
- Teams should evaluate whether the available support model provides sufficient guidance for their level of internal SOC 2 expertise.
- Complex enterprise governance requirements may extend beyond the platform’s primary focus on security compliance and certification workflows.
SOC 2 compliance software comparison
| Platform | Best for | Standout strengths |
| Scytale | SaaS organizations of all sizes with complex compliance needs seeking efficient AI GRC management processes | AI GRC compliance automation, continuous security and compliance monitoring, AI agents, multi-framework management, streamlined GRC processes, and expert guidance |
| Optro | Teams seeking structured compliance management | Centralized dashboards, workflows, and risk management |
| Apptega | Organizations managing multiple security frameworks | Framework crosswalking, multi-tenant management, and compliance reporting |
| LogicGate | Mature organizations with customized GRC programs | Configurable workflows, risk management, and framework crosswalks |
| OneTrust | Enterprises with broader privacy and data requirements | Privacy, data governance, risk assessment, and auditor collaboration |
| Qualys | Enterprises focused on technical security compliance | Asset discovery, configuration assessments, and technical control validation |
| Secureframe | Security teams automating SOC 2 compliance | Cloud scanning, workforce compliance, vendor management, and readiness assessments |
Streamline GRC workflows with no blind spots.
How to compare SOC 2 compliance platforms
Choosing the right SOC 2 compliance platform means considering how well it can help your organization achieve and maintain SOC 2 compliance, not just comparing feature lists. Here are the key areas to consider when evaluating your options:
Test the platform with your systems
Ask vendors to demonstrate evidence collection using the types of systems your organization relies on. This helps you understand the depth of integrations and how much evidence will still need to be collected or reviewed manually.
Review control and remediation workflows
Look at how the platform assigns control ownership, tracks evidence history, flags failed controls, and manages remediation. Teams should be able to see what requires attention, who owns it, and whether outstanding issues have been resolved.
Understand the auditor experience
Ask to see how auditors access evidence, submit requests, review documentation, and communicate with your team. A clear auditor workflow can reduce back-and-forth and make the SOC 2 assessment easier to manage.
Compare the level of support
Consider how much guidance is included beyond the software itself. Some solutions are primarily self-service, while others combine an AI compliance platform with expert support to help teams manage implementation, audit preparation, and ongoing compliance.
What are the key benefits of SOC 2 compliance software?
SOC 2 compliance software does more than simplify individual compliance tasks. When implemented effectively, it can improve how teams manage ownership, respond to issues, and maintain their compliance program over time. Key benefits include:
- Clearer accountability: Centralized task ownership and deadlines make it easier to see who is responsible for each control and what still needs attention.
- Faster issue resolution: Compliance gaps and failed controls can be surfaced and assigned quickly, helping teams resolve issues before they affect an audit.
- Better cross-team collaboration: Security, IT, HR, engineering, and compliance teams can work from the same information instead of coordinating through separate spreadsheets and email threads.
- Stronger audit history: A consistent record of evidence, control activity, approvals, and remediation gives teams and auditors a clearer view of how compliance has been maintained over time.
- Lower compliance costs: More efficient workflows can reduce the internal time and resources required to manage SOC 2 and help control overall SOC 2 compliance costs.
- Easier customer assurance: A well-maintained SOC 2 program makes it easier to demonstrate security practices during customer due diligence and security reviews.


How Scytale streamlines SOC 2 compliance
Scytale brings SOC 2 workflows into one centralized platform, helping teams reduce the administrative effort involved in managing compliance. Automated workflows streamline evidence collection, control tracking, risk management, and audit preparation, while continuous visibility helps teams address compliance gaps before they become larger issues.
Scytale combines its AI-powered compliance platform with dedicated GRC experts who provide hands-on guidance throughout the SOC 2 journey. This combination helps teams move through compliance faster, maintain audit readiness, and build a SOC 2 program that remains manageable as the organization grows.
FAQs about SOC 2 compliance software
Is SOC 2 compliance necessary for every type of company?
SOC 2 compliance is not required for every company, but it is particularly valuable for organizations that handle customer data or provide technology and cloud-based services. It helps demonstrate strong security practices and gives customers greater confidence in how their data is protected. SOC 2 can also support enterprise sales, where customers increasingly expect vendors to provide independent assurance of their security controls.
What are the top challenges SOC 2 compliance software solves?
SOC 2 compliance software helps solve challenges such as manual evidence collection, scattered documentation, unclear control ownership, and time-consuming audit preparation. By centralizing and automating these processes, top SOC 2 platforms like Scytale help teams reduce repetitive work, identify gaps earlier, and maintain compliance more efficiently.
How does SOC 2 compliance software enhance third-party trust?
SOC 2 compliance software helps organizations maintain the controls and evidence needed to demonstrate strong security practices to customers, partners, and other stakeholders. By keeping compliance information current and organized, it can simplify security reviews and due diligence while giving third parties greater confidence in how their data is protected.
What are the main features to look for in SOC 2 tools?
The main features to look for include automated evidence collection, continuous control monitoring, risk management, policy management, integrations, and audit management. These capabilities help teams maintain accurate compliance records, identify control gaps earlier, coordinate responsibilities, and stay prepared for SOC 2 assessments throughout the year.
Can I use these tools for other frameworks like ISO 27001 or GDPR?
Yes, many SOC 2 compliance tools also support additional security and privacy frameworks such as ISO 27001, GDPR, and HIPAA. Scytale’s AI GRC platform supports multi-framework cross-mapping, allowing teams to reuse relevant controls and evidence across different requirements. This reduces duplicate work and makes it easier to manage multiple compliance programs from one place.


